

AI
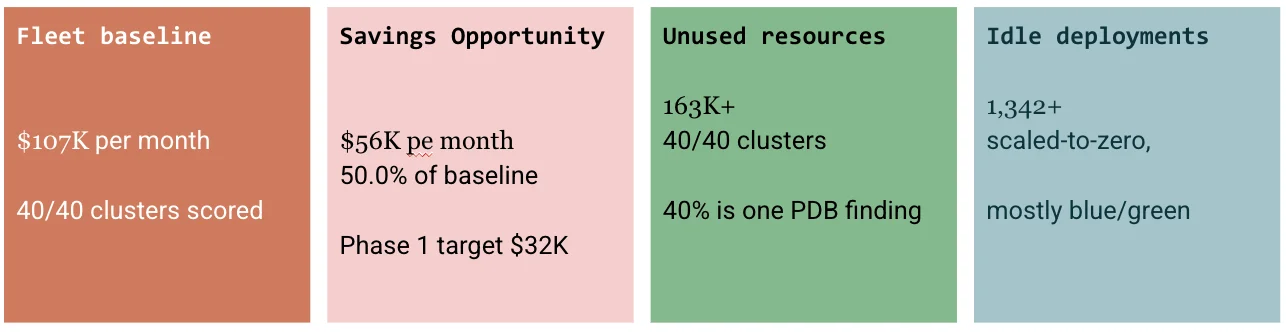
Nirmata’s Cloud Agents Audited a 40-Cluster Kubernetes Fleet, and recovered 40% of the Cost
Nirmata’s Cloud Agents Audited a 40-Cluster Kubernetes Fleet, and recovered 40% of the Cost
6 min read
Tag
19 posts
AI
Nirmata’s Cloud Agents Audited a 40-Cluster Kubernetes Fleet, and recovered 40% of the Cost
6 min read
Engineering
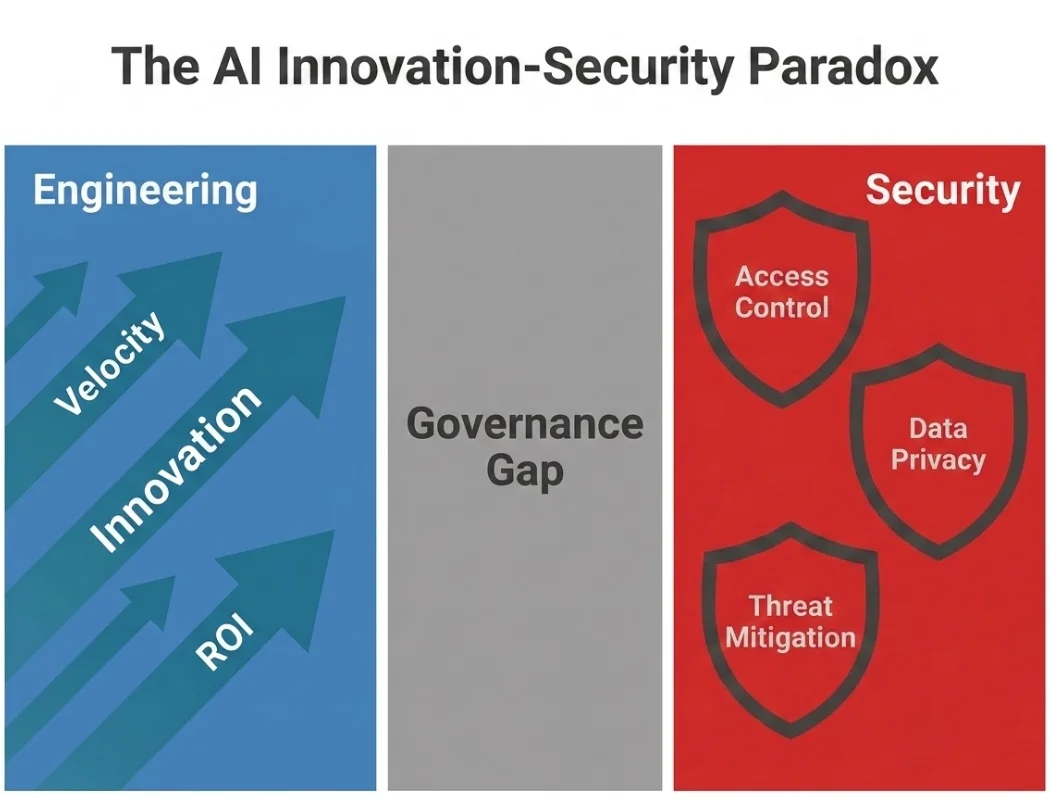
Nirmata's AI Controls provides real-time governance, policy enforcement and risk management, bridging the gap between engineering and security leaders.
4 min read
Engineering
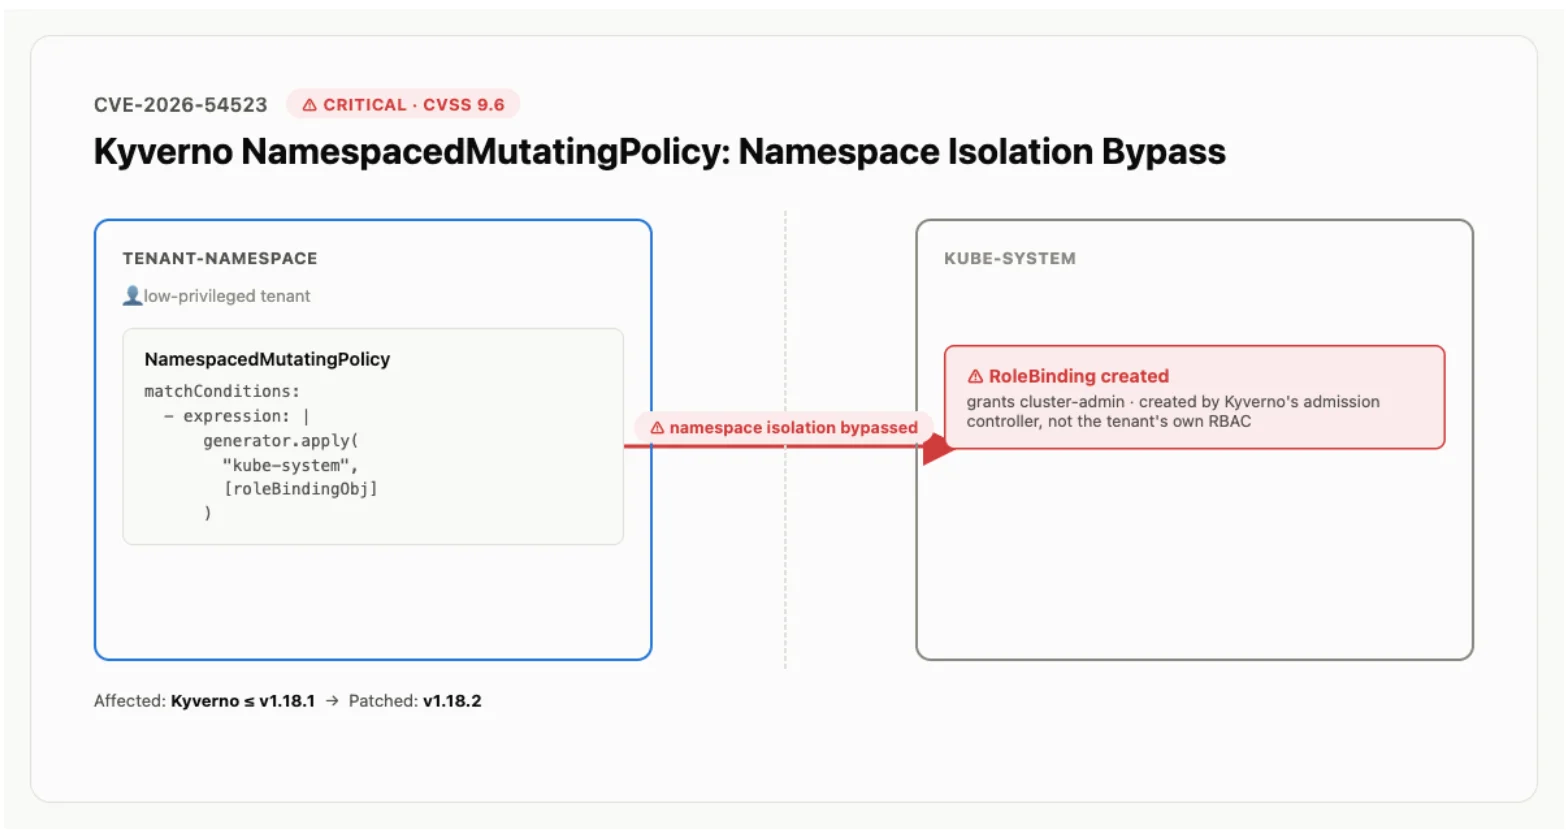
CVE-2026-54523 (CVSS 9.6) lets a Kyverno NamespacedMutatingPolicy create resources in any namespace. Kyverno 1.18.0 and 1.18.1 are affected; upgrade to 1.18.2.
3 min read
AI
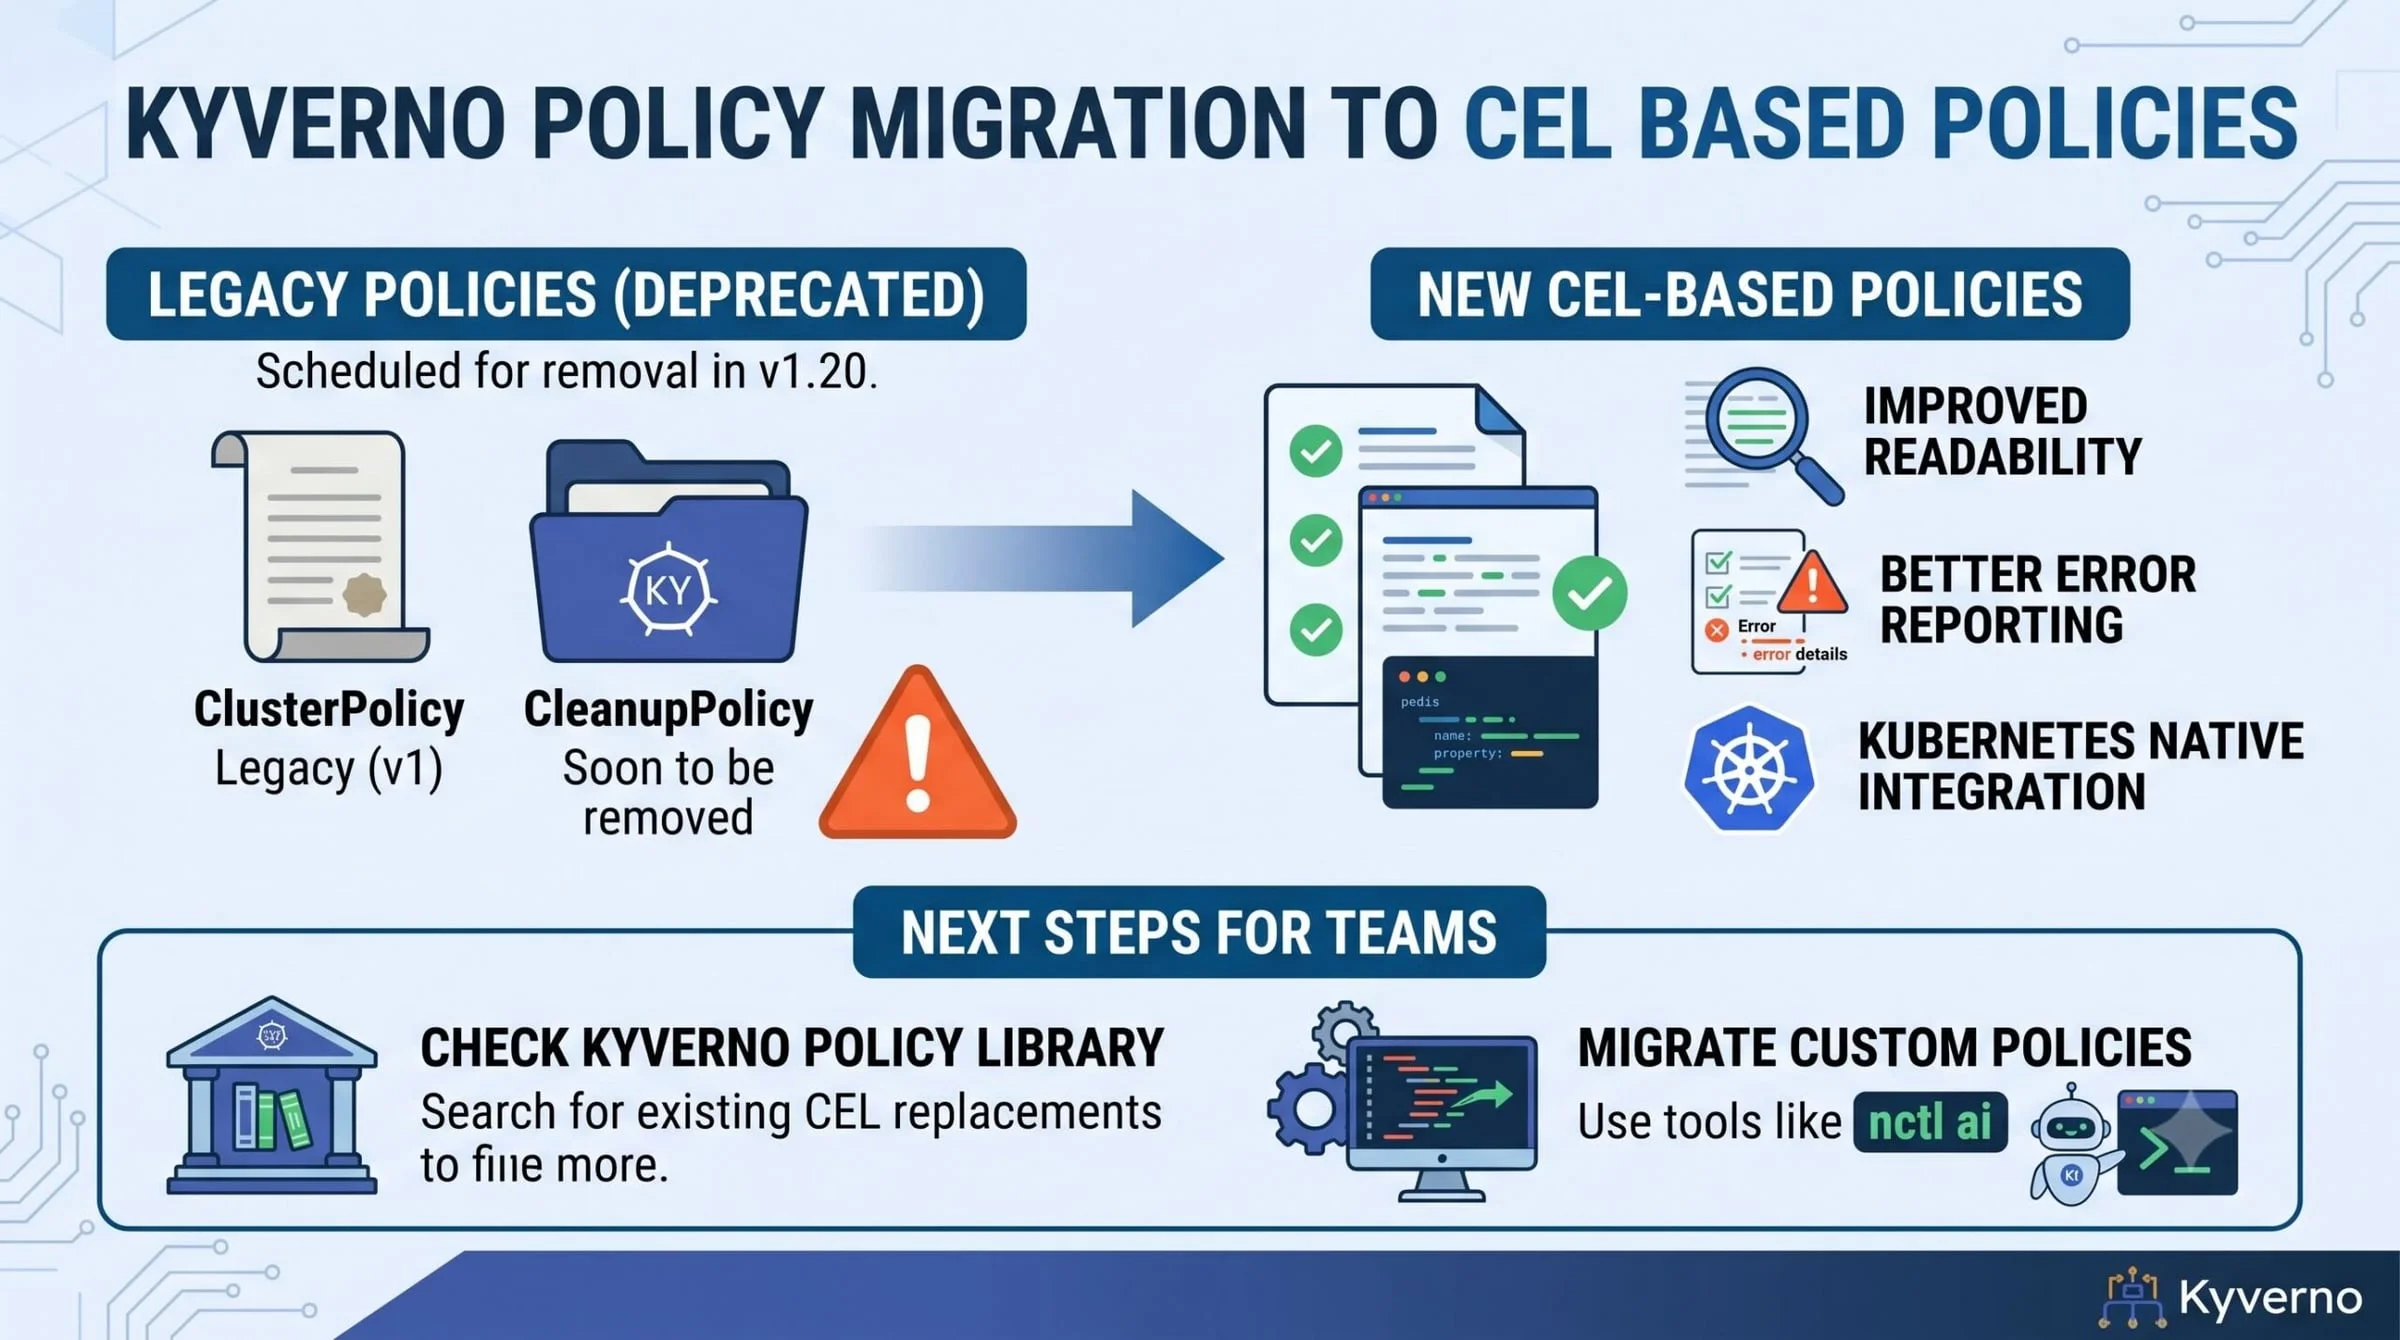
Quick question: the last time a Kyverno policy rejected a resource, did the error actually tell you why — or did you spend twenty minutes squinting at a pattern block…
6 min read
Events
We are very excited to announce that team Nirmata is a Silver sponsor of KubeCon + CloudNativeCon Europe 2024 from March 19-22. Our team is all geared up for this event…
5 min read
Events
Meet us in 6 Sessions, 1 workshop, 2 booths! Kubecon+CloudNativeCon is a global flagship event organized by CNCF(Cloud Native Computing Foundation) which is a part of the…
5 min read
Business
Platform teams implement policy-based guardrails for Kubernetes environments on Day-0 to avoid resets, unexpected costs and downtime. Nirmata explains here.
5 min read
News
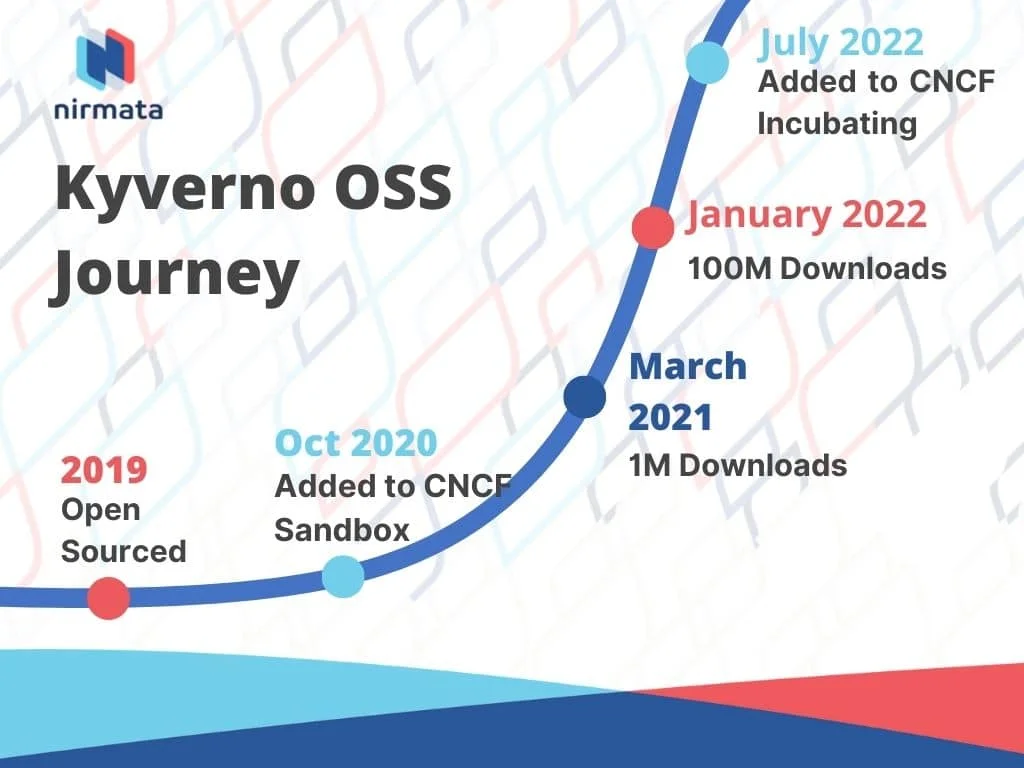
As Kyverno approaches its 2nd birthday, Nirmata marks this significant milestone with the exciting news that the project has moved from sandbox to incubating status!
3 min read
Engineering
CVE-2021-25742 lets ingress-nginx users with Ingress access read all cluster secrets via snippets. Upgrade to v1.0.1 or v0.49.1 and disable snippet annotations.
3 min read
News
New features includes: Cosign, ForEach, CLI test, Dynamic Webhooks.
3 min read
Kyverno
Nirmata is pleased to officially announce the release of the newest version of project Kyverno, a popular policy engine for Kubernetes utilization. Meet Kyverno 1.4.2…
3 min read
Kyverno
Kyverno officially becomes a CNCF sandbox project, demonstrating Nirmata’s commitment to accelerating adoption of cloud-native technologies.
3 min read