Introduction In our previous blog post, we delved into the importance of addressing CVEs within application libraries and outlined strategies for remediation. Continuing…
CVE-2022-47633 let a malicious registry slip unsigned images past verifyImages in Kyverno 1.8.3 and 1.8.4. Upgrade to 1.8.5 and allow trusted registries only.
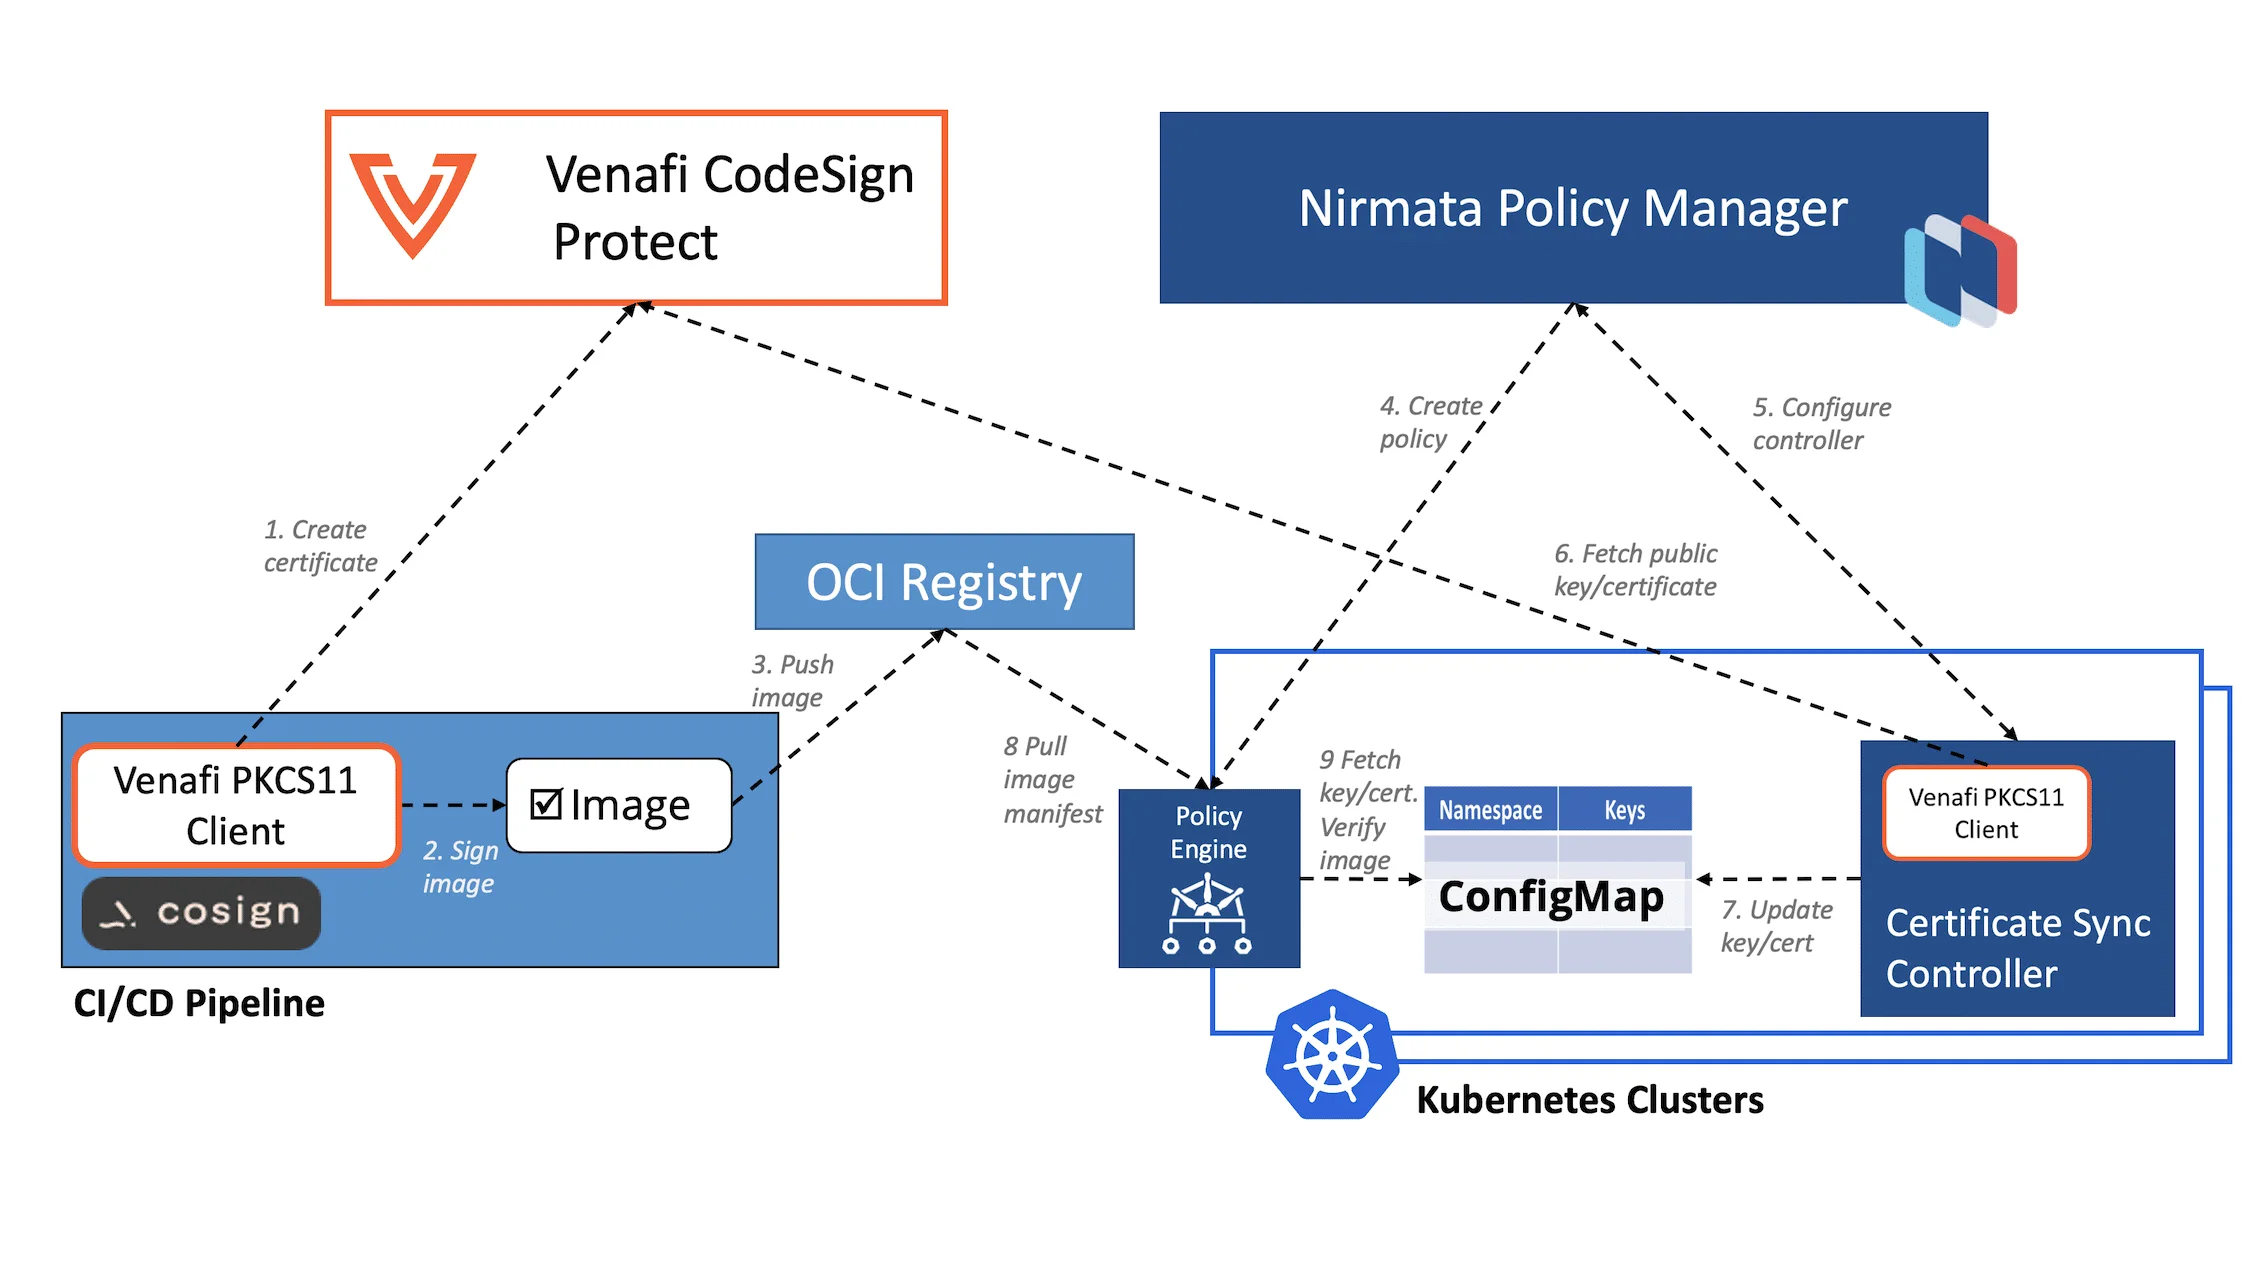
Securing software supply chains is a top priority for DevOps teams. Nirmata discuss how supply chain security can be implemented using Nirmata Policy Manager and Venafi…
Nirmata delivers this blog post describing how to enable image verification capability with Kyverno and Cosign on Amazon EKS, in order to obtain software supply chain…
Read this joint blog post from Dan Lorenc, a software engineer at Google and a maintainer of Cosign, and Jim Bugwadia, co-founder of Nirmata and a maintainer of Kyverno.