Why Ansible is Essential for Modern DevOps In today's fast-paced software development world, automation is crucial for maintaining speed, consistency, and scalability…
Get CVE-free container images: scan with Trivy, trace each library with Gradle dependencyInsight, then upgrade, force or replace it, and fail CI on new CVEs.
Introduction Recently, Akamai's Tomer Peled announced a security threat to Kubernetes clusters, CVE-2023-5528. A user who can create pods and persistent volumes on…
Preventive security stops misconfigurations before deployment, while detection and response catches threats at runtime. How they differ and why you need both.
Ingress users can steal ingress-nginx credentials via CVE-2023-5043, CVE-2023-5044 and CVE-2022-4886. Upgrade to v1.9.0 and block the annotations with Kyverno.
Kubernetes is designed for extensibility and allows several types of policies to be configured. In this post, we introduce the four types of policies available in…
Nirmata takes an in-depth look at the security and compliance challenges that organizations face with Kubernetes, and explores some solutions in our latest blog post.
Kubernetes is designed for extensibility and allows several types of policies to be configured. In this post, we introduce the four types of policies available in…
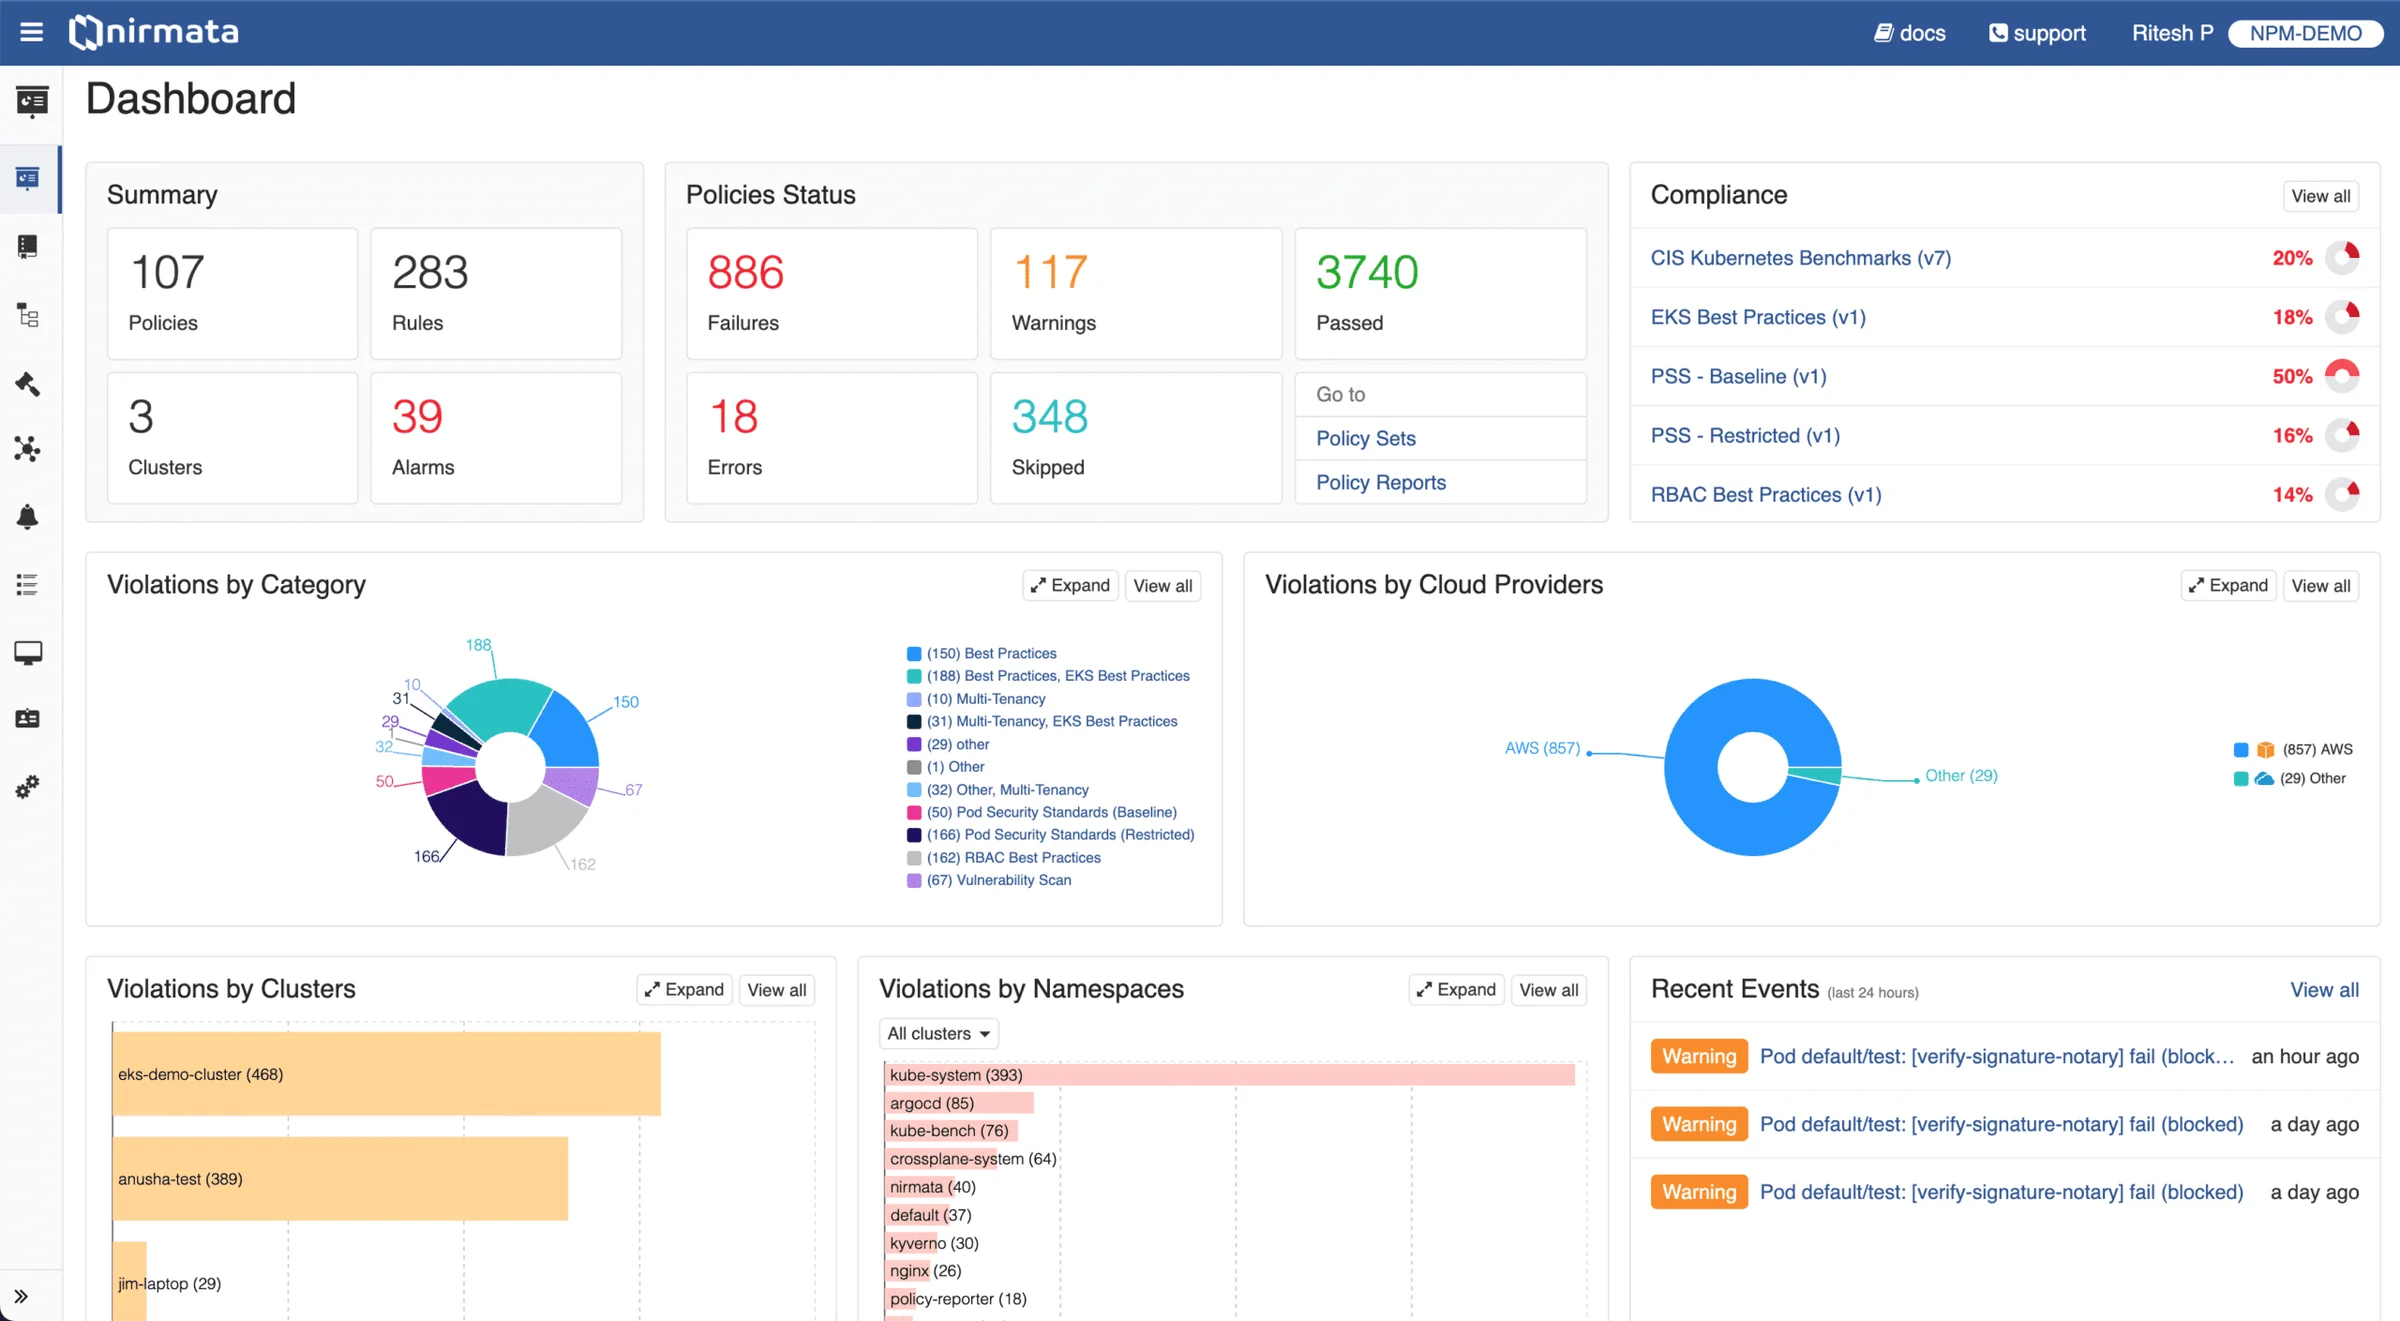
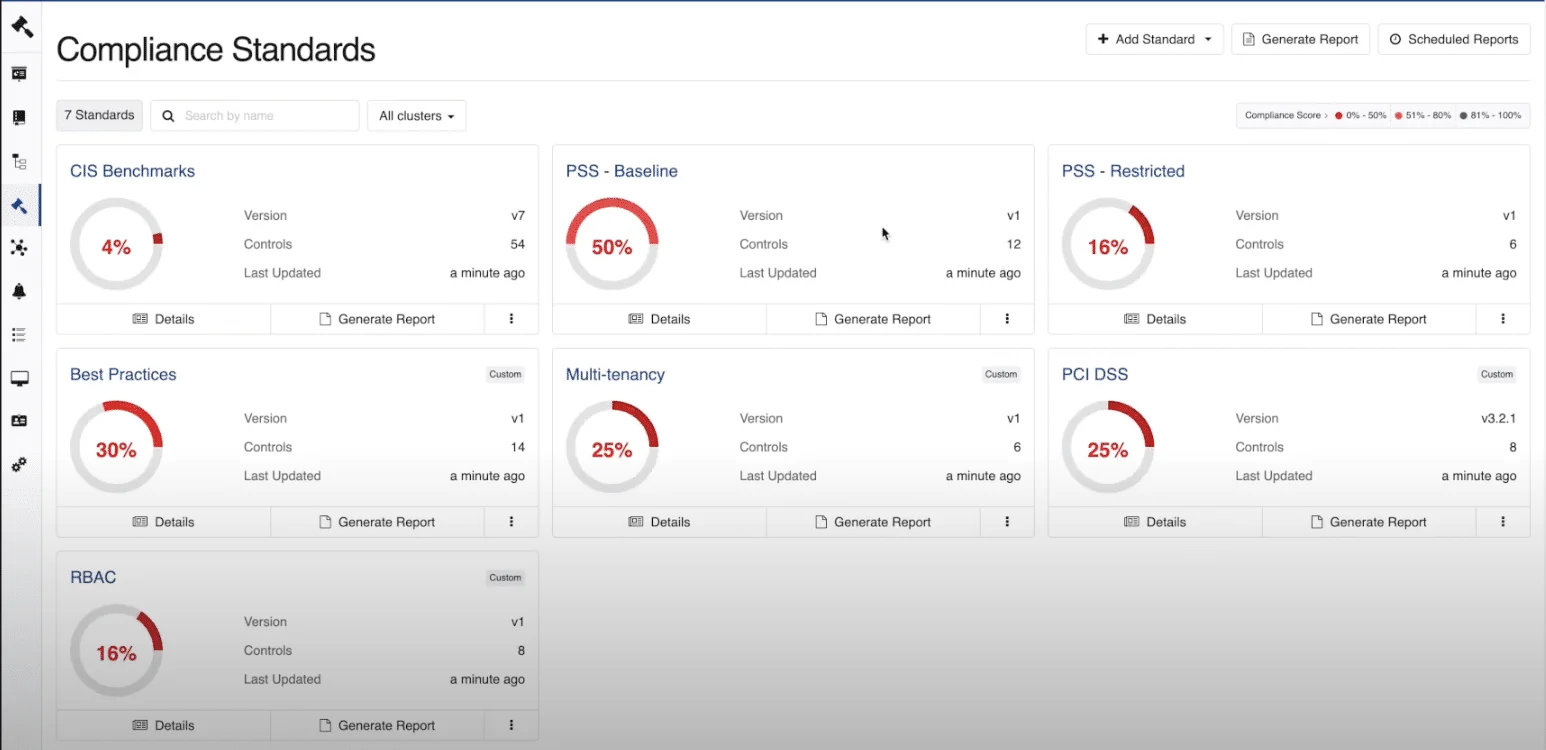
Nirmata Control Hub is a powerful solution that helps platform engineers with security, compliance, governance, and self-service automation for Kubernetes management.
Nirmata Control Hub has the required governance, security, and continuous compliance to build scalable Kubernetes-based platforms efficiently with K8s clusters!