

AI
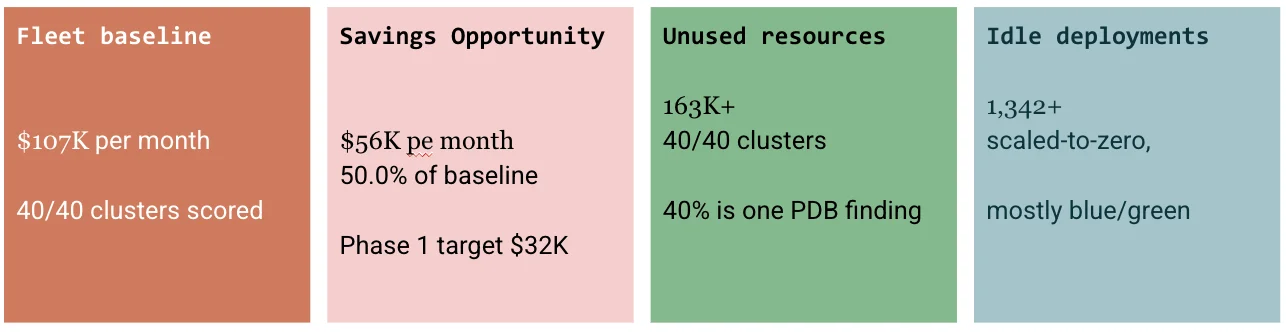
Nirmata’s Cloud Agents Audited a 40-Cluster Kubernetes Fleet, and recovered 40% of the Cost
Nirmata’s Cloud Agents Audited a 40-Cluster Kubernetes Fleet, and recovered 40% of the Cost
6 min read
Tag
186 posts · Page 2 of 16
AI
Nirmata’s Cloud Agents Audited a 40-Cluster Kubernetes Fleet, and recovered 40% of the Cost
6 min read
Engineering
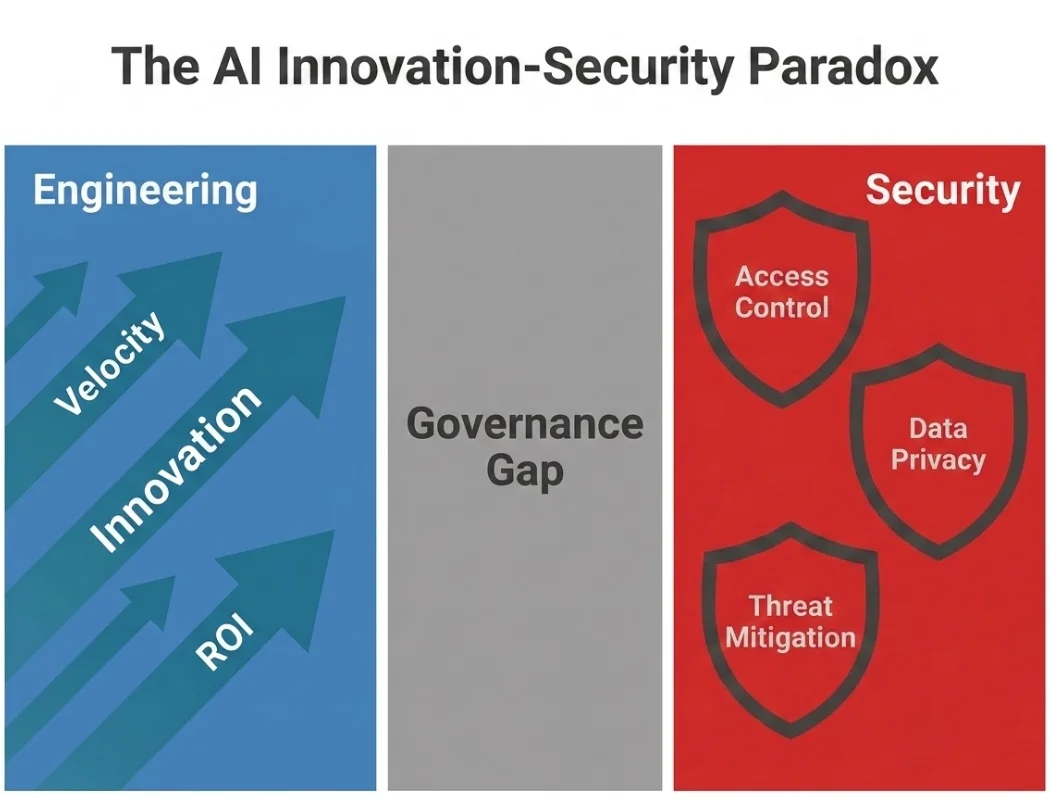
Nirmata's AI Controls provides real-time governance, policy enforcement and risk management, bridging the gap between engineering and security leaders.
4 min read
Engineering
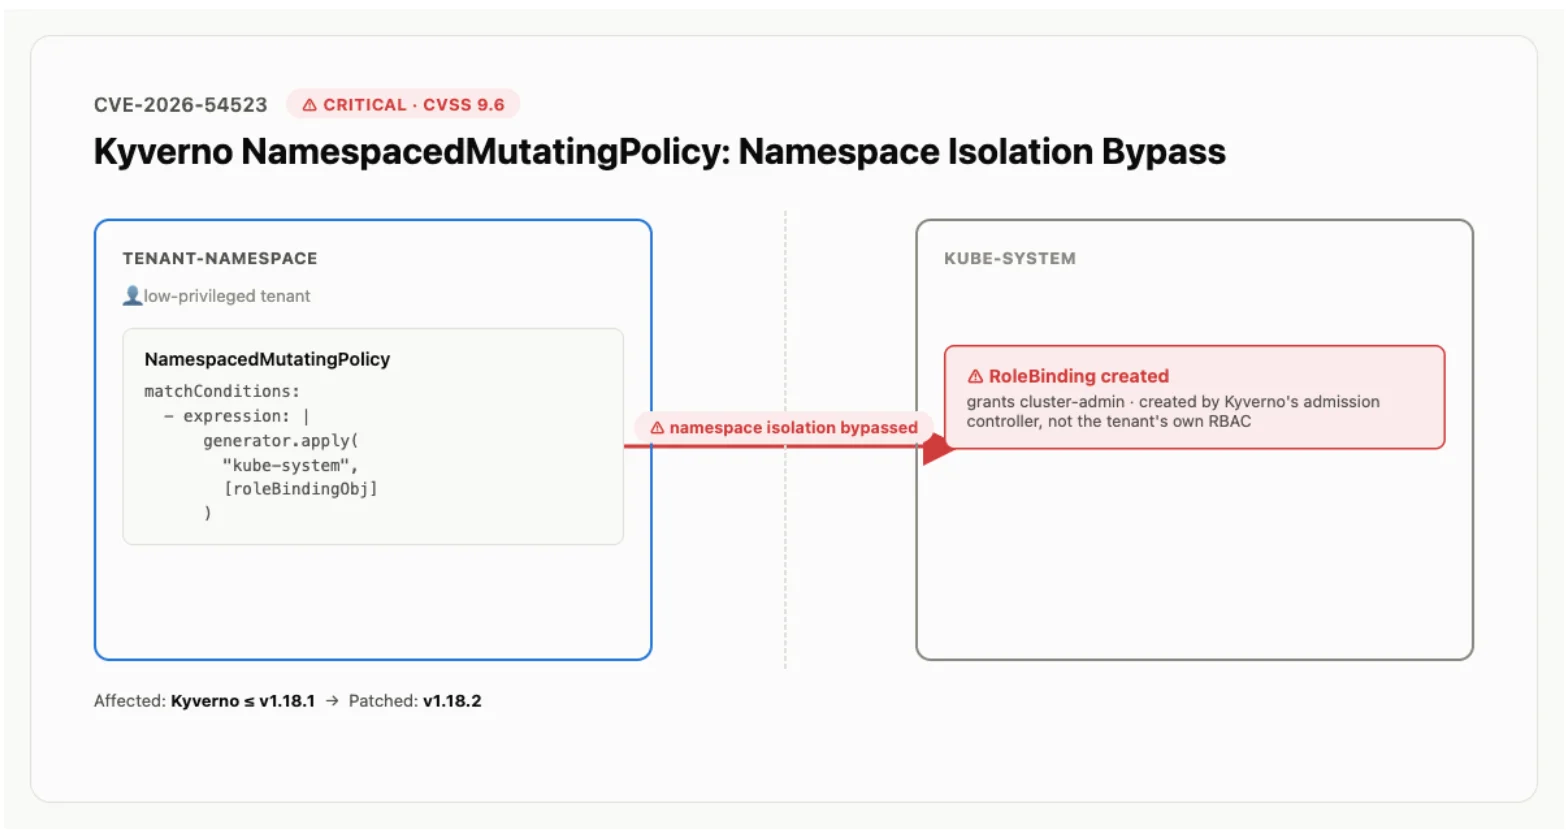
CVE-2026-54523 (CVSS 9.6) lets a Kyverno NamespacedMutatingPolicy create resources in any namespace. Kyverno 1.18.0 and 1.18.1 are affected; upgrade to 1.18.2.
3 min read
AI
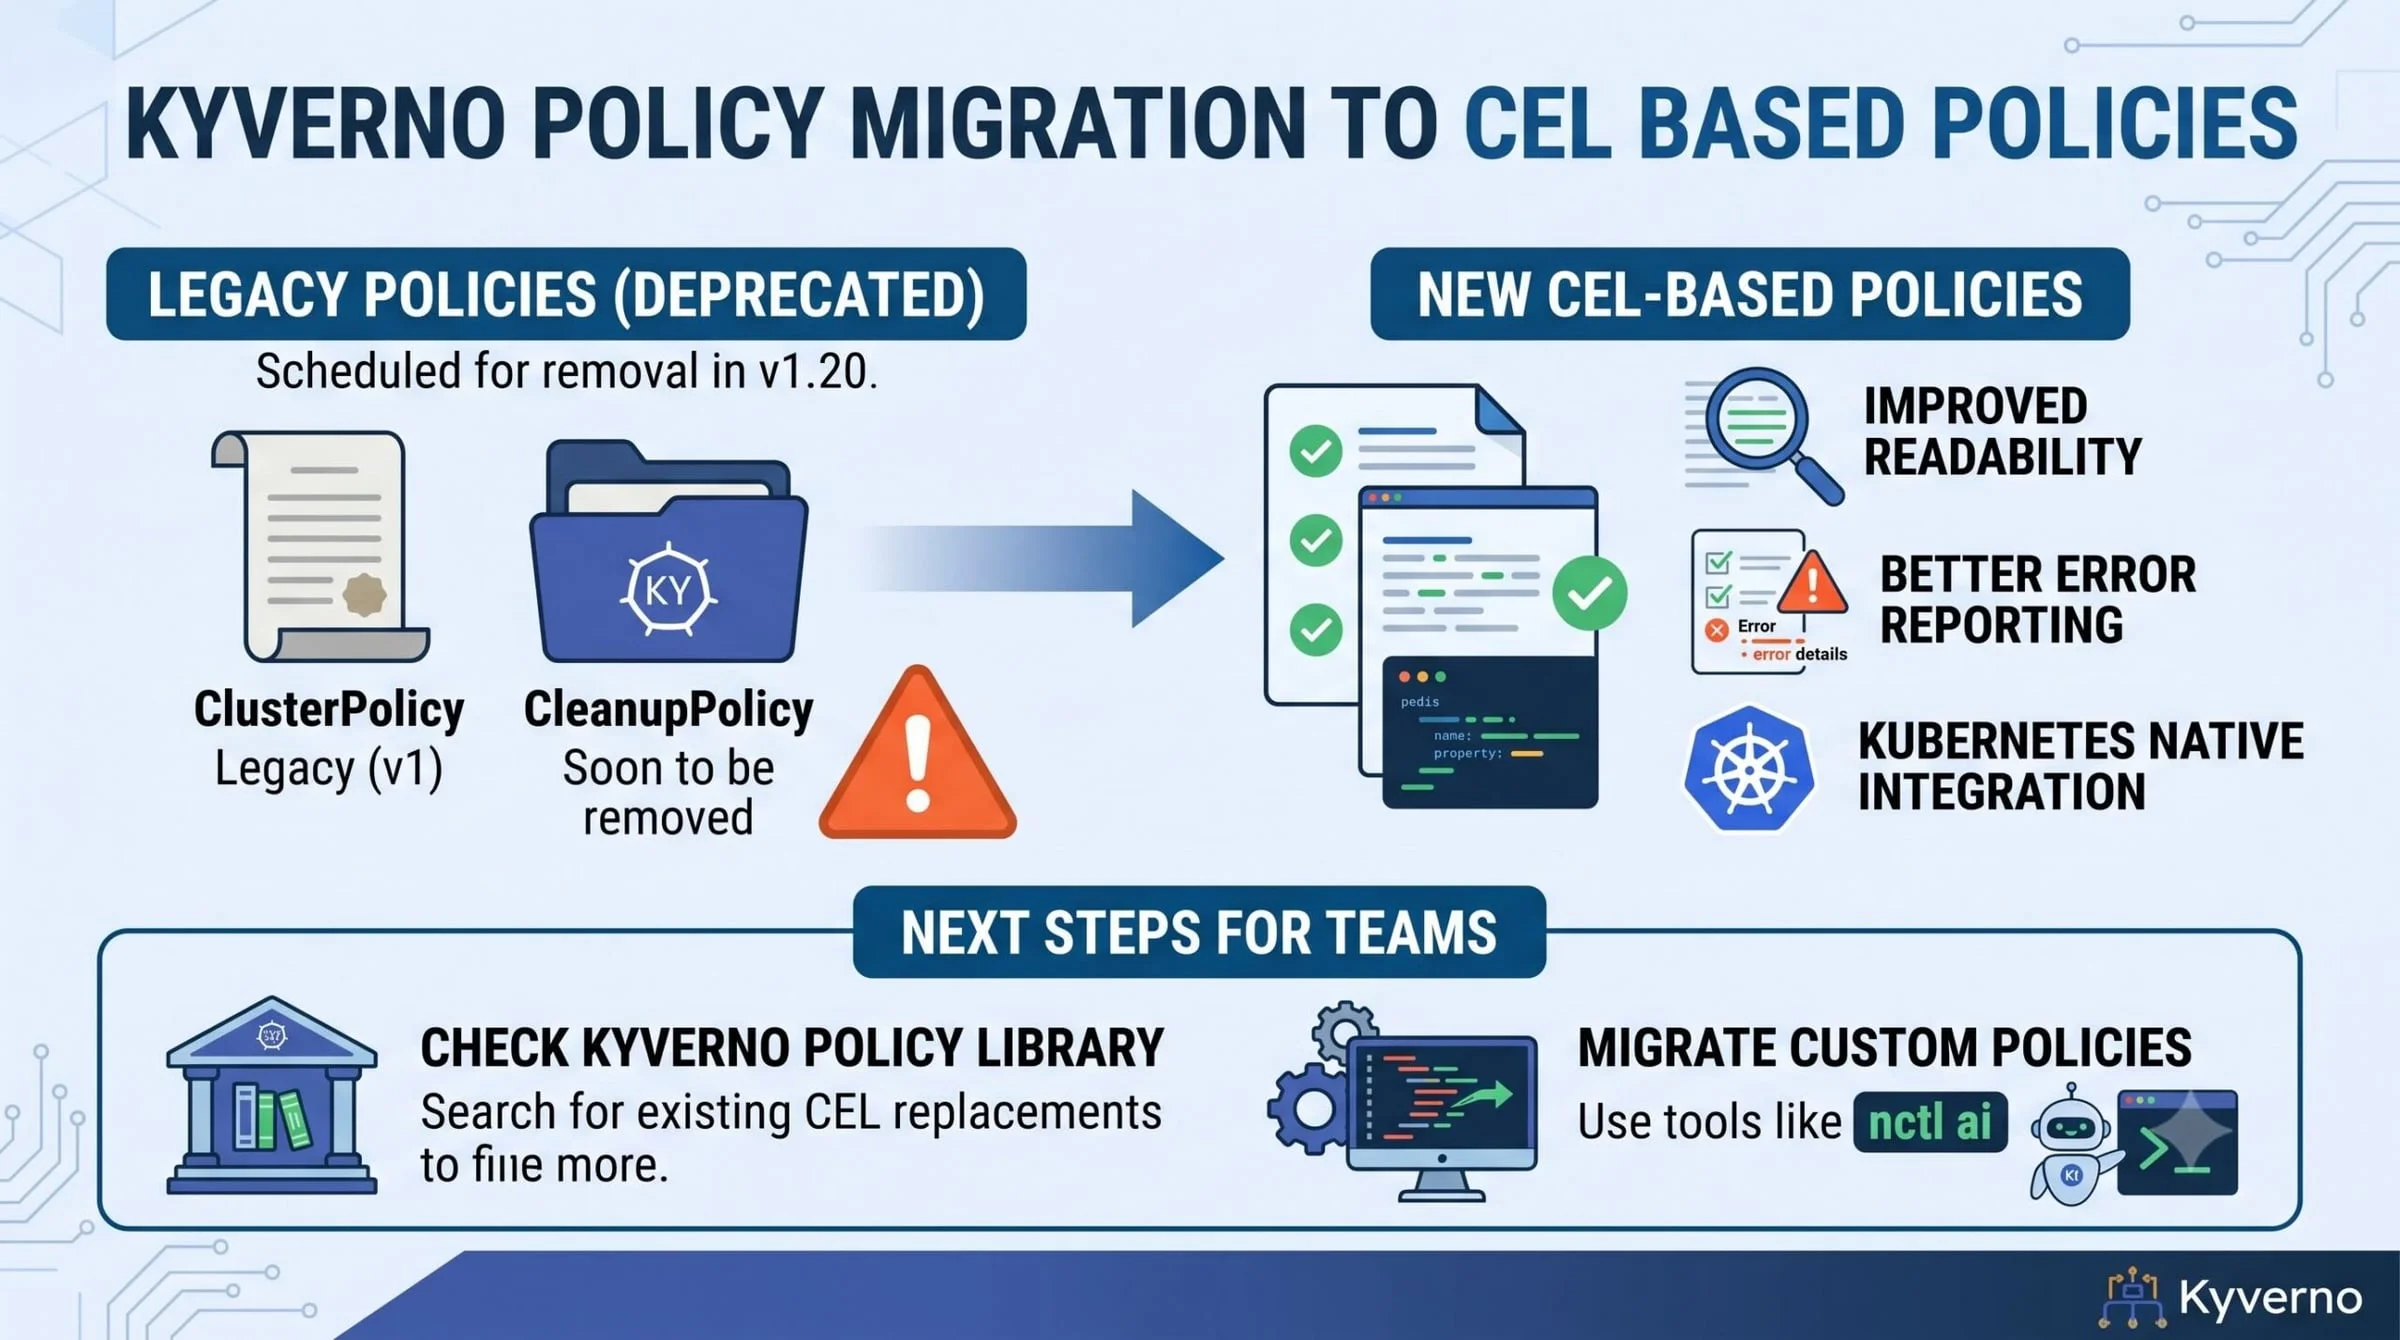
Quick question: the last time a Kyverno policy rejected a resource, did the error actually tell you why — or did you spend twenty minutes squinting at a pattern block…
6 min read
Kyverno
Learn why Kyverno is still essential alongside Kubernetes native policies for reporting, testing, automation, shift-left security, and complex policy logic.
6 min read
Kubernetes
Recently, CNCF's Cloud Native Live hosted an insightful session titled "Optimizing Cost, Performance, And Security In K8s With Policy-As-Code" featuring Anusha Hegde…
5 min read
Business
As 2024 draws to a close, we at Nirmata are taking a moment to reflect on a year filled with remarkable achievements and advancements in Kubernetes security, governance…
3 min read
Other
Nirmata participated in KubeCon India, one of the largest gatherings of cloud-native pros, developers, and the open-source community. Our team delivered several Kyverno…
2 min read
Kubernetes
Policy-as-code defines security, compliance and operational rules as versioned code that runs automatically. Here are 10 reasons cloud-native teams rely on it.
5 min read
Product
Read the latest on the critical role of policy-as-code and IaC in modern application security. Embed security in the very fabric of the Dev process. Nirmata explains…
3 min read
Kyverno
Nirmata explores how large financial institutions can leverage policy-as-code, using Kyverno - the Kubernetes-native policy engine - for better governance and security.
4 min read
Business
Policy-as-code allows platform engineering teams to define, manage, and enforce policies for security, compliance, and operational requirements. Nirmata explains here.
3 min read