

Engineering
XZ: A Case Study in Open-Source Supply Chain Attacks
CVE-2024-3094 is a CVSS 10.0 backdoor in XZ Utils 5.6.0 and 5.6.1. Downgrade to 5.4.6 or move to 5.6.2, then block affected images with a Kyverno policy.
6 min read
Category
129 posts · Page 3 of 11
Engineering
CVE-2024-3094 is a CVSS 10.0 backdoor in XZ Utils 5.6.0 and 5.6.1. Downgrade to 5.4.6 or move to 5.6.2, then block affected images with a Kyverno policy.
6 min read
Engineering
Leaky Vessels (CVE-2024-21626) lets a container reach the host filesystem through runc 1.1.11 and earlier. Patch to runc 1.1.12 and audit nodes with Kyverno.
7 min read
Engineering
This blog post was co-authored by Khaled Emara. About Kyverno Kyverno is a policy engine designed for Kubernetes and cloud native workloads. Policies can be managed as…
9 min read
Engineering
Google Kubernetes Engine (GKE) is a popular tool for managing containerized applications. However, a critical vulnerability has been discovered in GKE that could allow…
2 min read
Engineering
In today's age of advanced technology platforms, organizations must proactively prioritize security concerns across all teams and platforms. Nirmata offers an efficient…
1 min read
Engineering
This blog describes how we successfully transitioned our container workloads from AMD to ARM processors and discusses the benefits and trade offs.
5 min read
Engineering
This blog post discusses how to generate Kubernetes Validating Admission Policies from Kyverno policies.
4 min read
Engineering
Ingress users can steal ingress-nginx credentials via CVE-2023-5043, CVE-2023-5044 and CVE-2022-4886. Upgrade to v1.9.0 and block the annotations with Kyverno.
3 min read
Engineering
Kyverno, in simple terms, is a policy engine designed for Kubernetes that can be used to describe policies and validate resource requests against those policies. It…
7 min read
Engineering
In this post, we will show you how the Kyverno CLI can now be used to apply/test Kubernetes Validating Admission Policies that were first introduced in 1.26.
3 min read
Engineering
Kubernetes is designed for extensibility and allows several types of policies to be configured. In this post, we introduce the four types of policies available in…
4 min read
Engineering
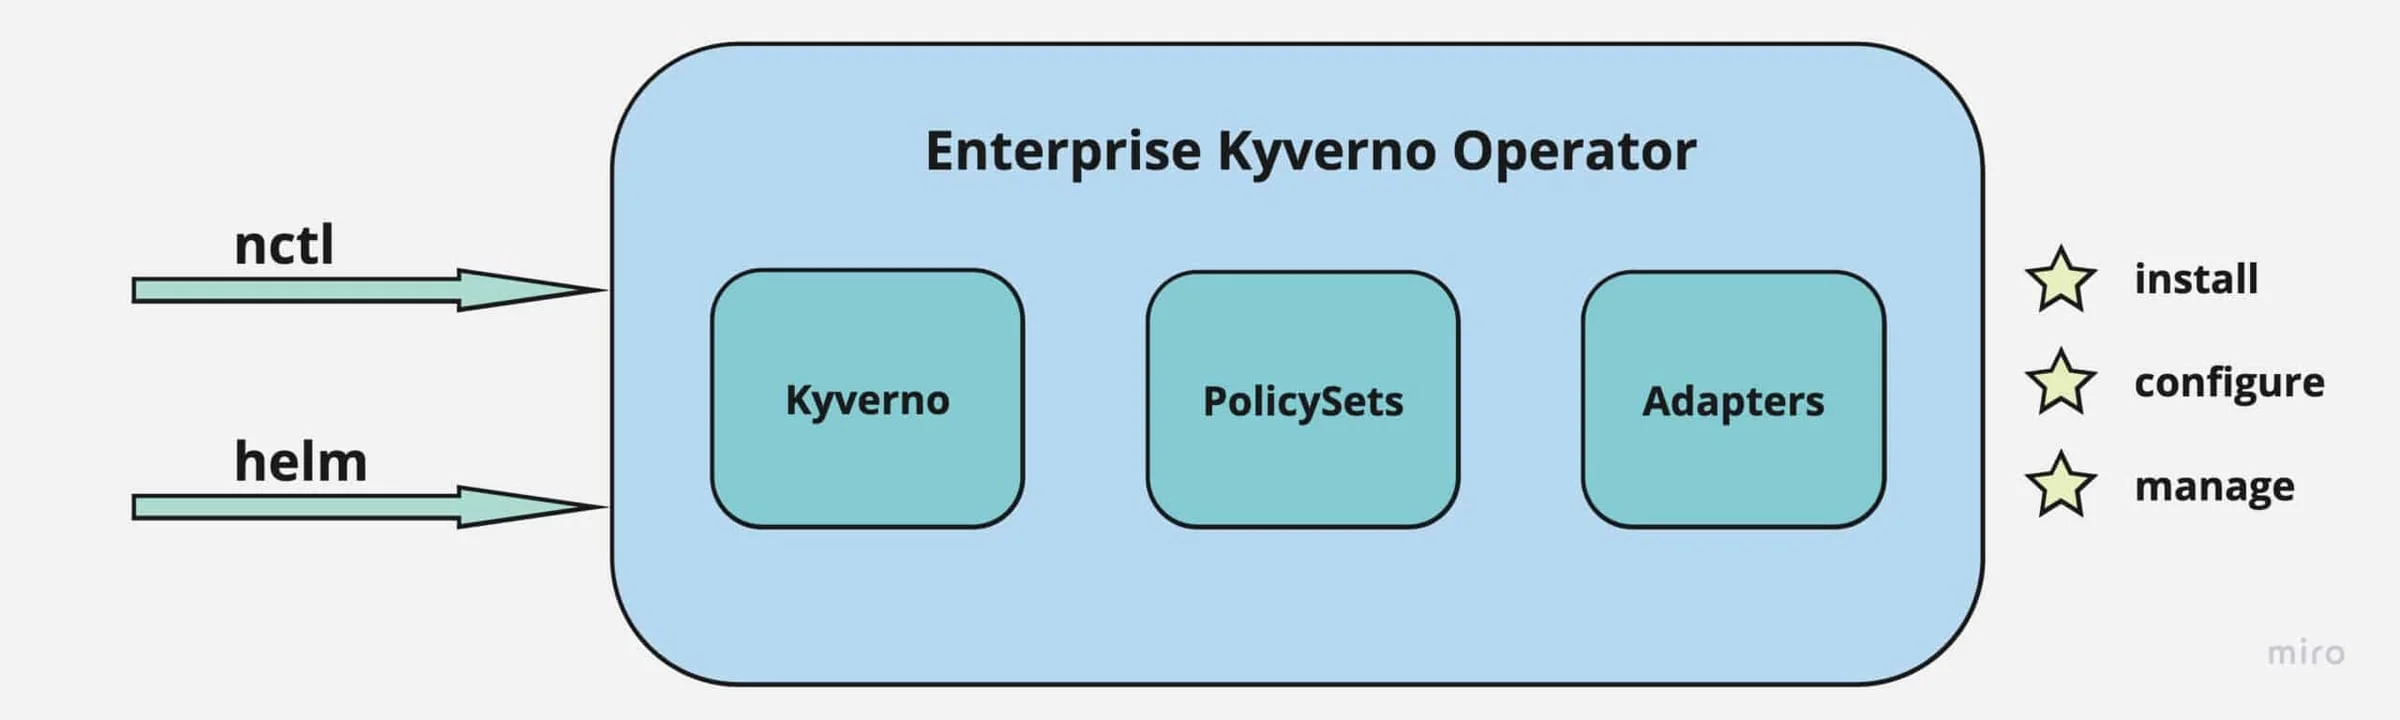
The Enterprise Kyverno Operator offers comprehensive lifecycle management capabilities that go beyond Kyverno itself, extending to related components like policies and…
6 min read