Engineering
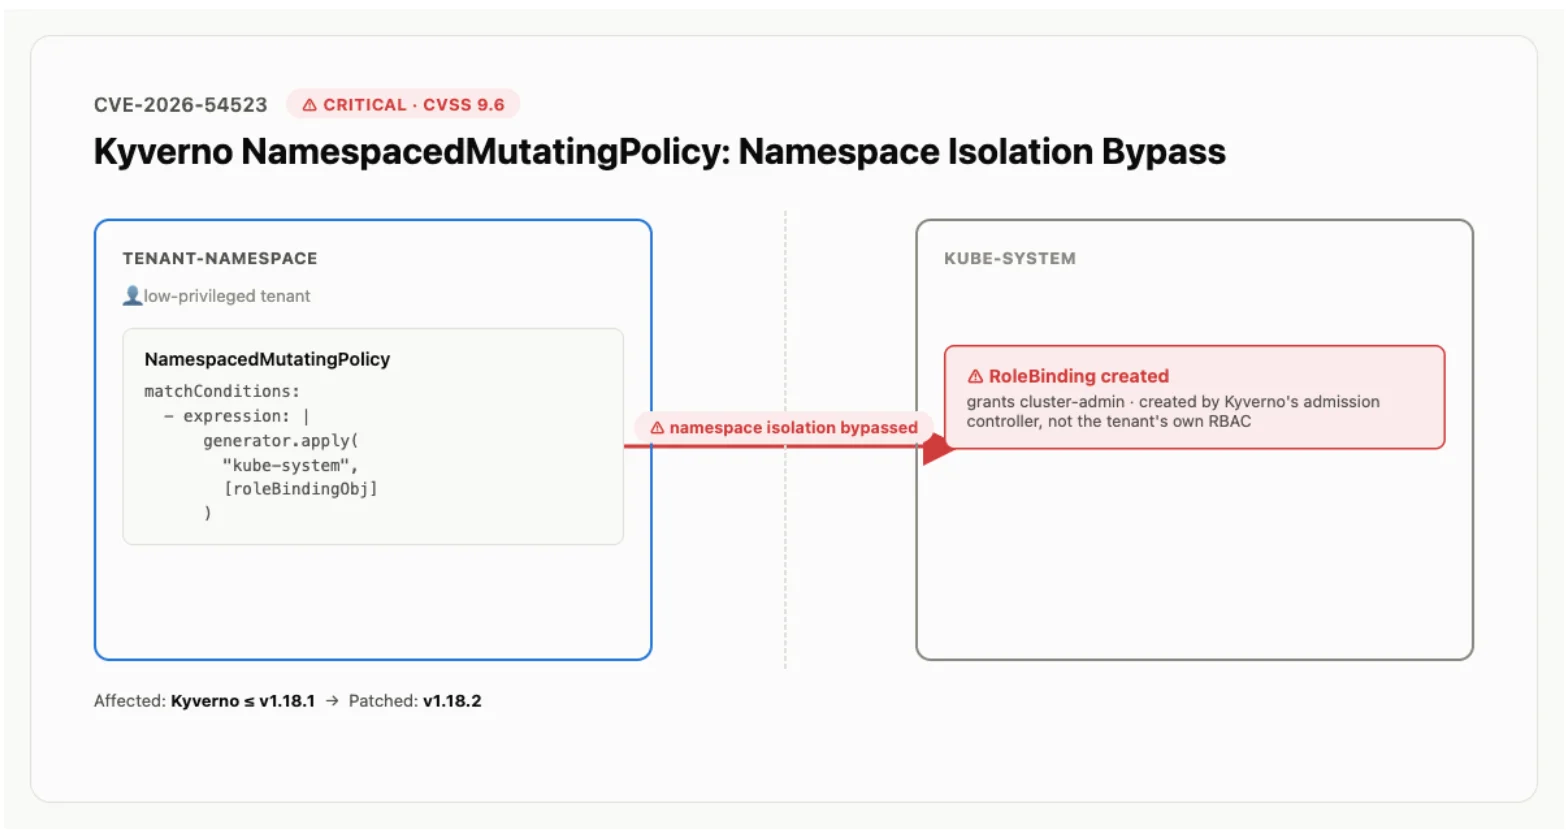
Critical Kyverno Vulnerability — CVE-2026-54523
CVE-2026-54523 (CVSS 9.6) lets a Kyverno NamespacedMutatingPolicy create resources in any namespace. Kyverno 1.18.0 and 1.18.1 are affected; upgrade to 1.18.2.
3 min read
Tag
2 posts
Engineering
CVE-2026-54523 (CVSS 9.6) lets a Kyverno NamespacedMutatingPolicy create resources in any namespace. Kyverno 1.18.0 and 1.18.1 are affected; upgrade to 1.18.2.
3 min read
AI
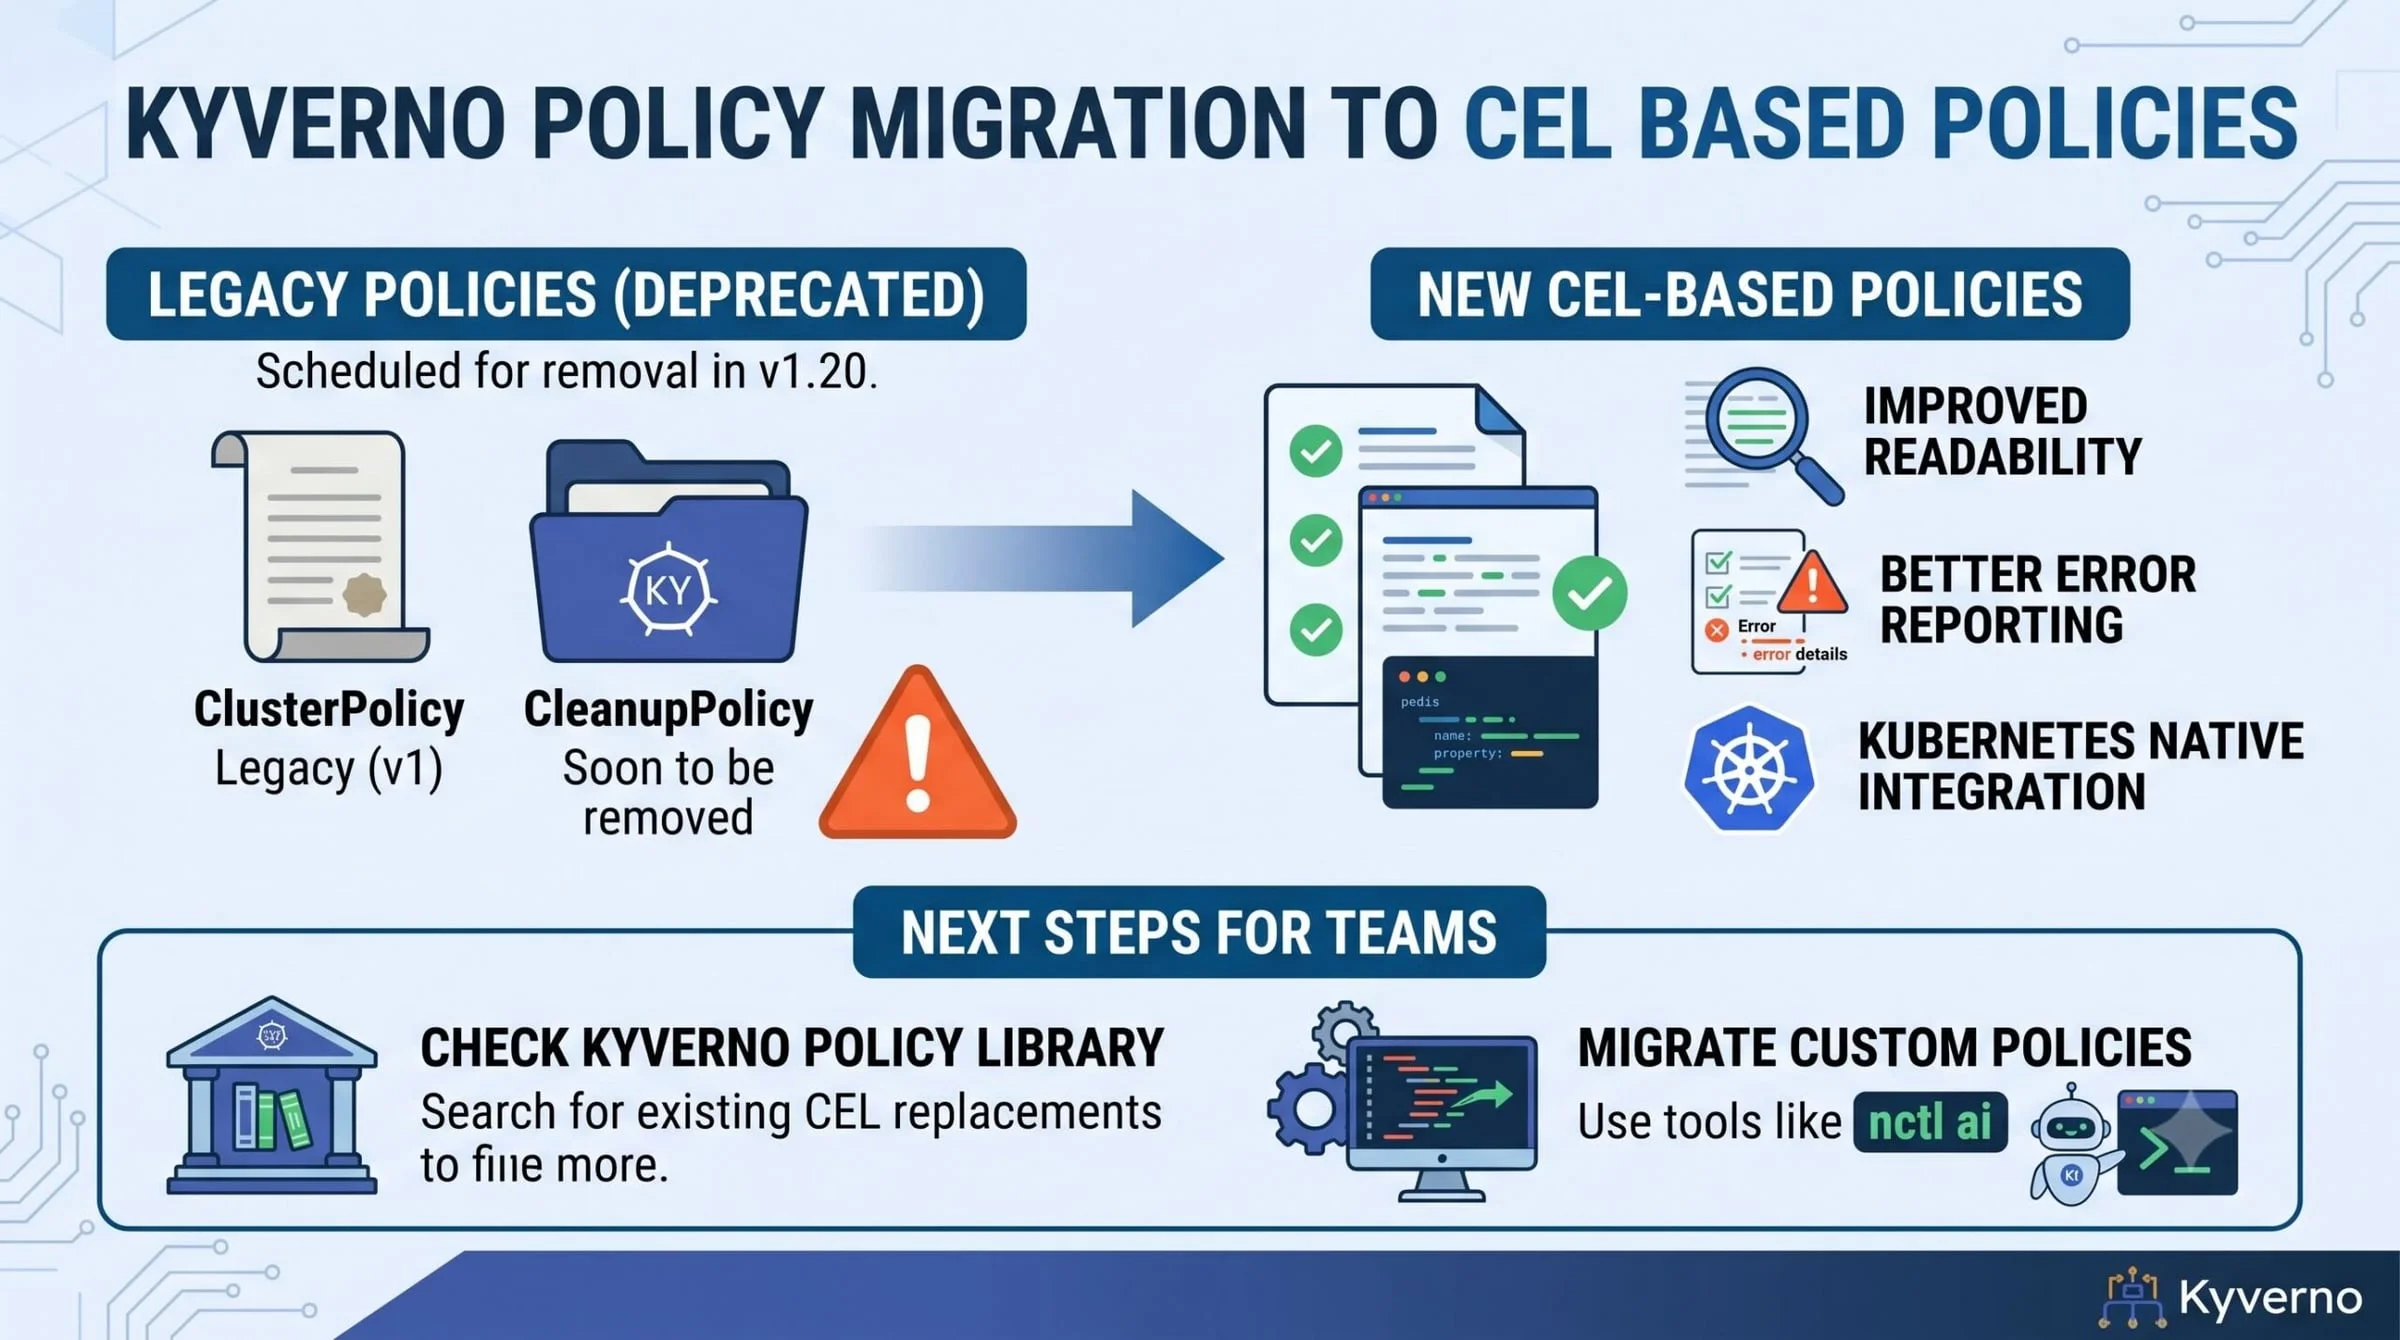
Quick question: the last time a Kyverno policy rejected a resource, did the error actually tell you why — or did you spend twenty minutes squinting at a pattern block…
6 min read