Jim Bugwadia, co-founder of Nirmata, shares five must-have policies that Kubernetes administrators should consider to enhance their cluster security and efficiency, with…
As an exhibitor and participant at KubeCon 2024, Nirmata was thrilled to engage with the Kubernetes community, share our latest advancements, and experience the energy of…
Policy-as-code defines security, compliance and operational rules as versioned code that runs automatically. Here are 10 reasons cloud-native teams rely on it.
Read the latest on the critical role of policy-as-code and IaC in modern application security. Embed security in the very fabric of the Dev process. Nirmata explains…
Nirmata explores how large financial institutions can leverage policy-as-code, using Kyverno - the Kubernetes-native policy engine - for better governance and security.
PolicyReport API The Policy Report API was developed under the Kubernetes Policy Working Group and provides an API that can be used by any policy engine, security…
As with any IaC, scanning OpenTofu files is crucial for ensuring security, reliability, and compliance of cloud infrastructure deployments. Kyverno by Nirmata can help.
Guest Contributors: Benoit Schipper (HCS), Marcel Booms (HCS) OpenShift’s Built-In Security Features OpenShift is renowned for its robust out-of-the-box security…
Introduction Policy Reports are used by Kyverno to store the result of policies and cluster policies that match a resource. Kyverno generates reports during admission…
Introduction Recently, Akamai's Tomer Peled announced a security threat to Kubernetes clusters, CVE-2023-5528. A user who can create pods and persistent volumes on…
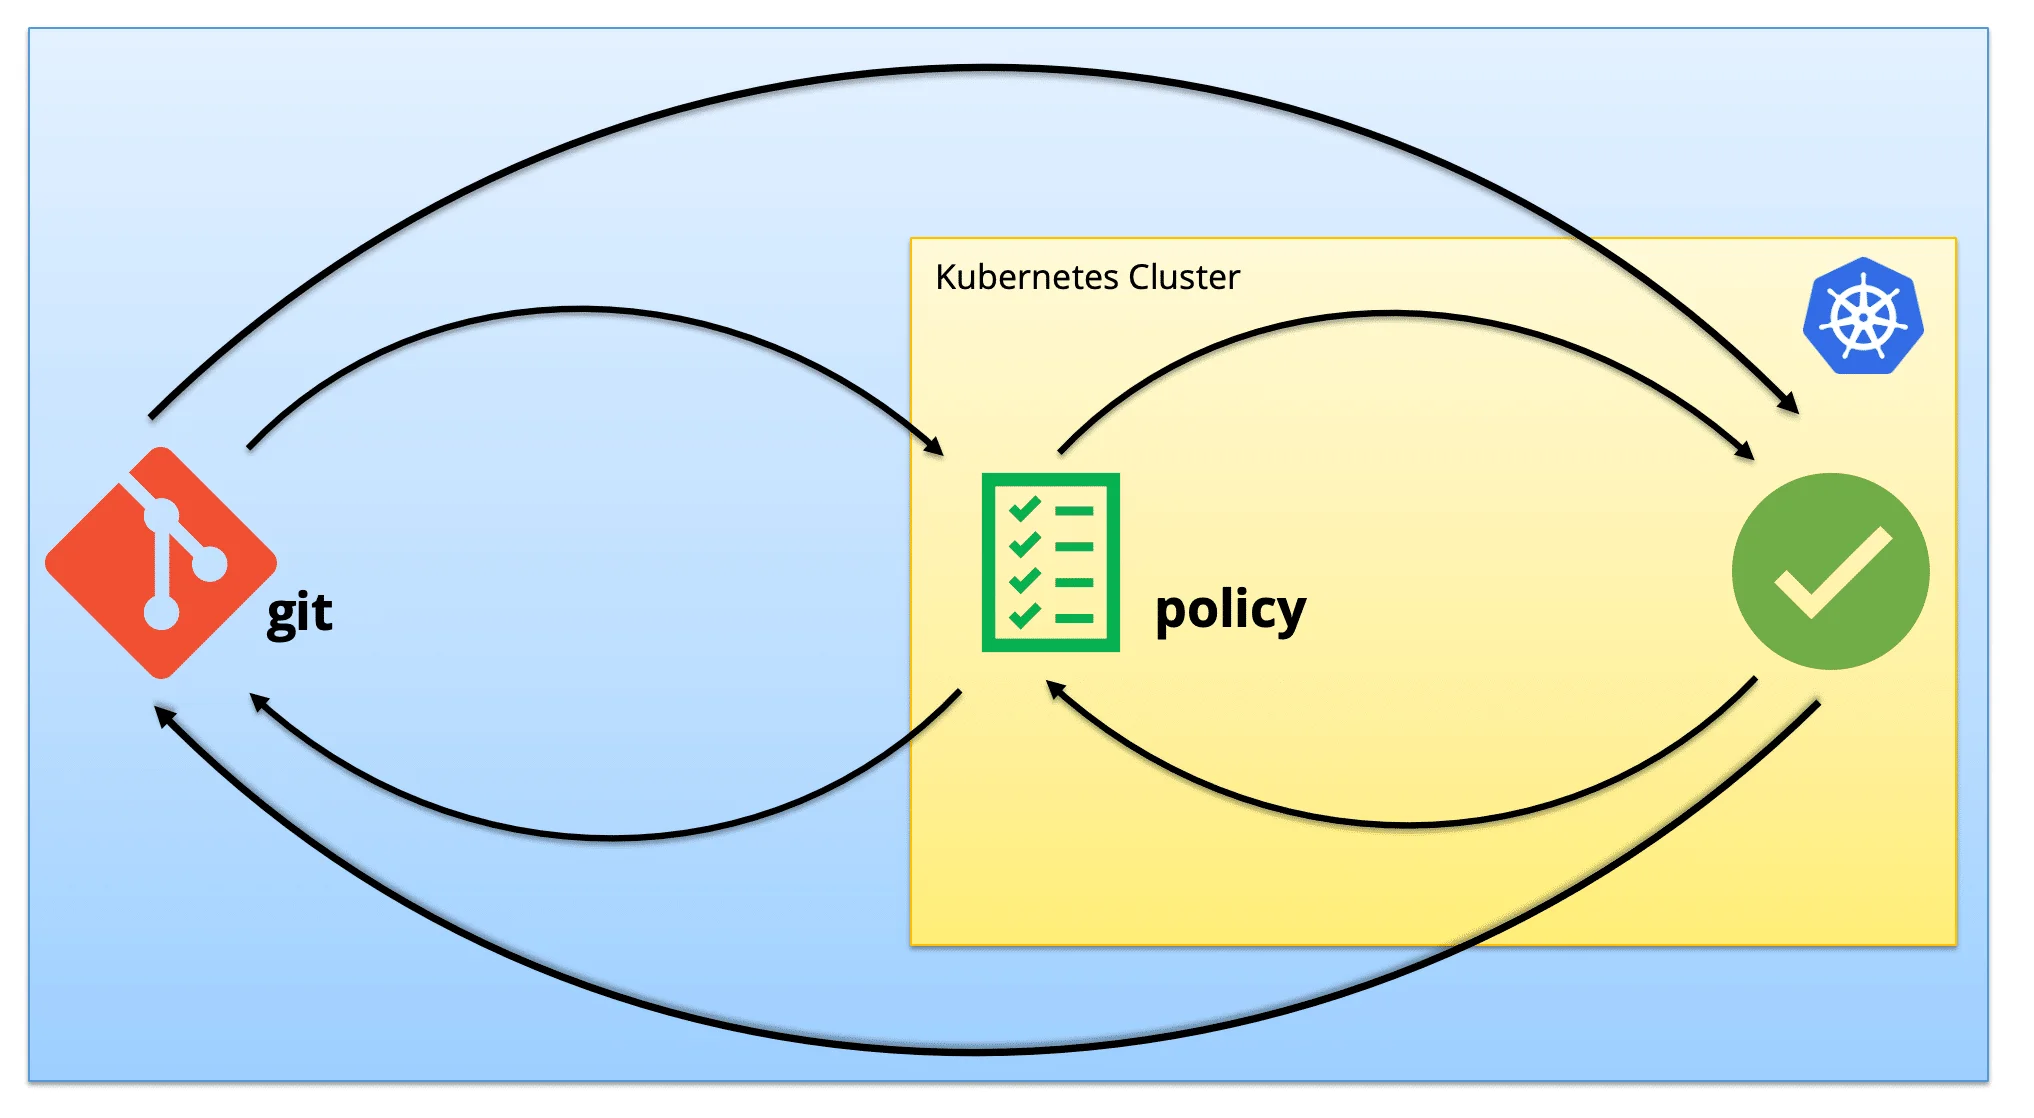
Do policies that mutate or generate resources violate GitOps principles? In this blog post, I will show you how policy-based resource management can be complementary to…
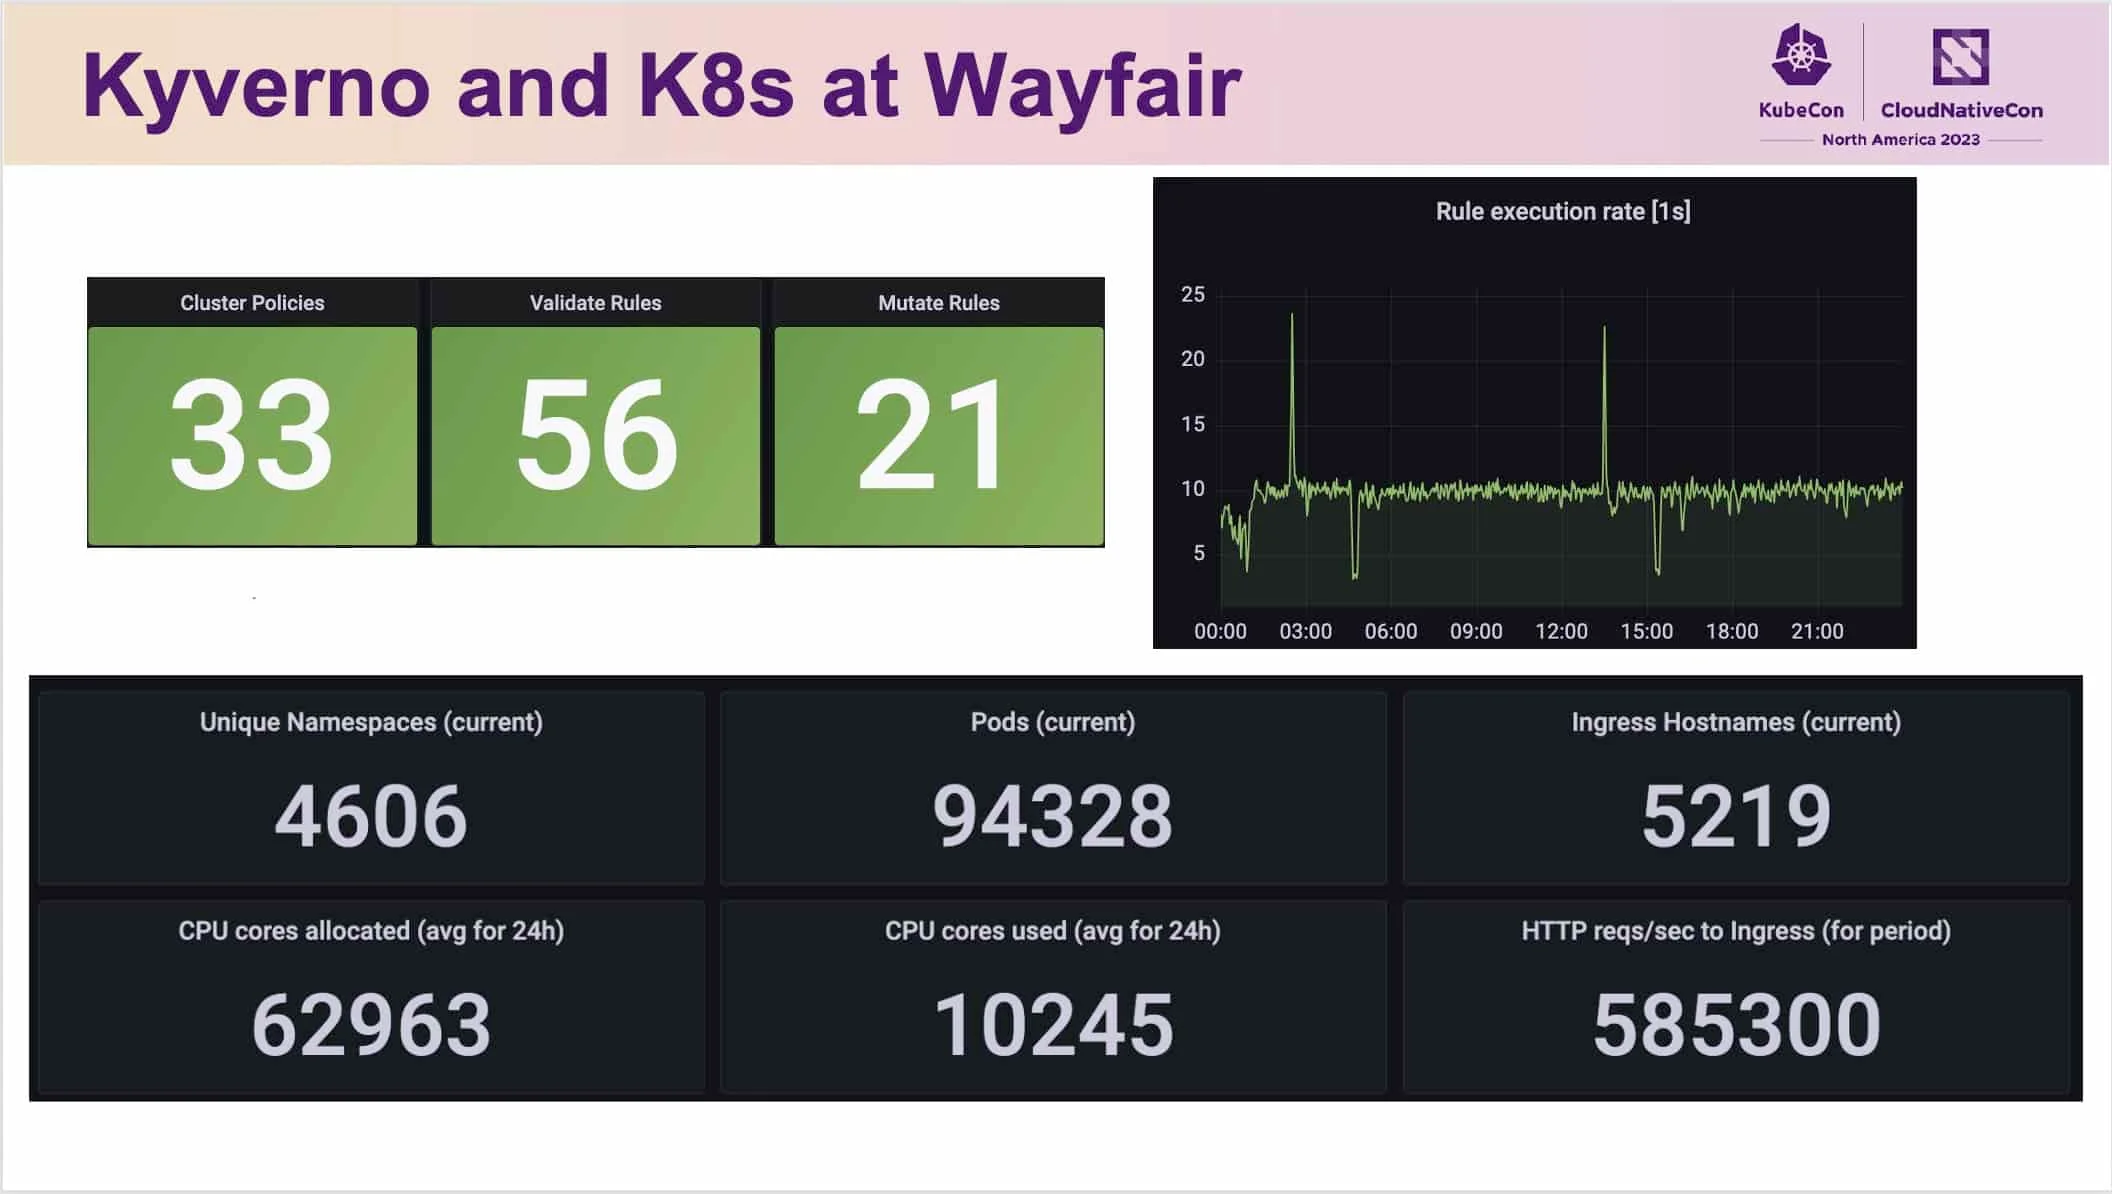
This blog post summarizes the recent Kubecon presentation by Zach Swanson at Wayfair, in which he shared key insights and reasons for migrating to Kyverno.