Nirmata is thrilled to introduce Cloud Control Point, a revolutionary Cloud governance solution bringing admission control to the Cloud to prevent misconfigurations…
We are announcing a new feature in the Nirmata Control Hub - Offline Cluster Scanning. You can now scan any Kubernetes cluster without installing agents.
Why Ansible is Essential for Modern DevOps In today's fast-paced software development world, automation is crucial for maintaining speed, consistency, and scalability…
AWS CDK: Bringing Flexibility to Cloud Infrastructure The AWS Cloud Development Kit (CDK) is an open-source framework that enables developers to define cloud…
PolicyReport API The Policy Report API was developed under the Kubernetes Policy Working Group and provides an API that can be used by any policy engine, security…
Guest Contributors: Benoit Schipper (HCS), Marcel Booms (HCS) OpenShift’s Built-In Security Features OpenShift is renowned for its robust out-of-the-box security…
What is a Policy Exception Often, only some policies and rules the security or platform team defines are universally applicable. Sometimes, a developer needs an exception…
Why Scan Pipelines? Scanning CI/CD pipelines i.e. Git repositories for misconfigurations is crucial for ensuring the security and reliability of your software projects…
Applying security policies in CI pipelines ensures that security measures are integrated into the development process from the outset, reducing the risk of introducing…
Nirmata Control Hub streamlines policy exception management for enterprise DevSecOps teams. Powered by Kyverno - a popular CNCF policy engine created by Nirmata.
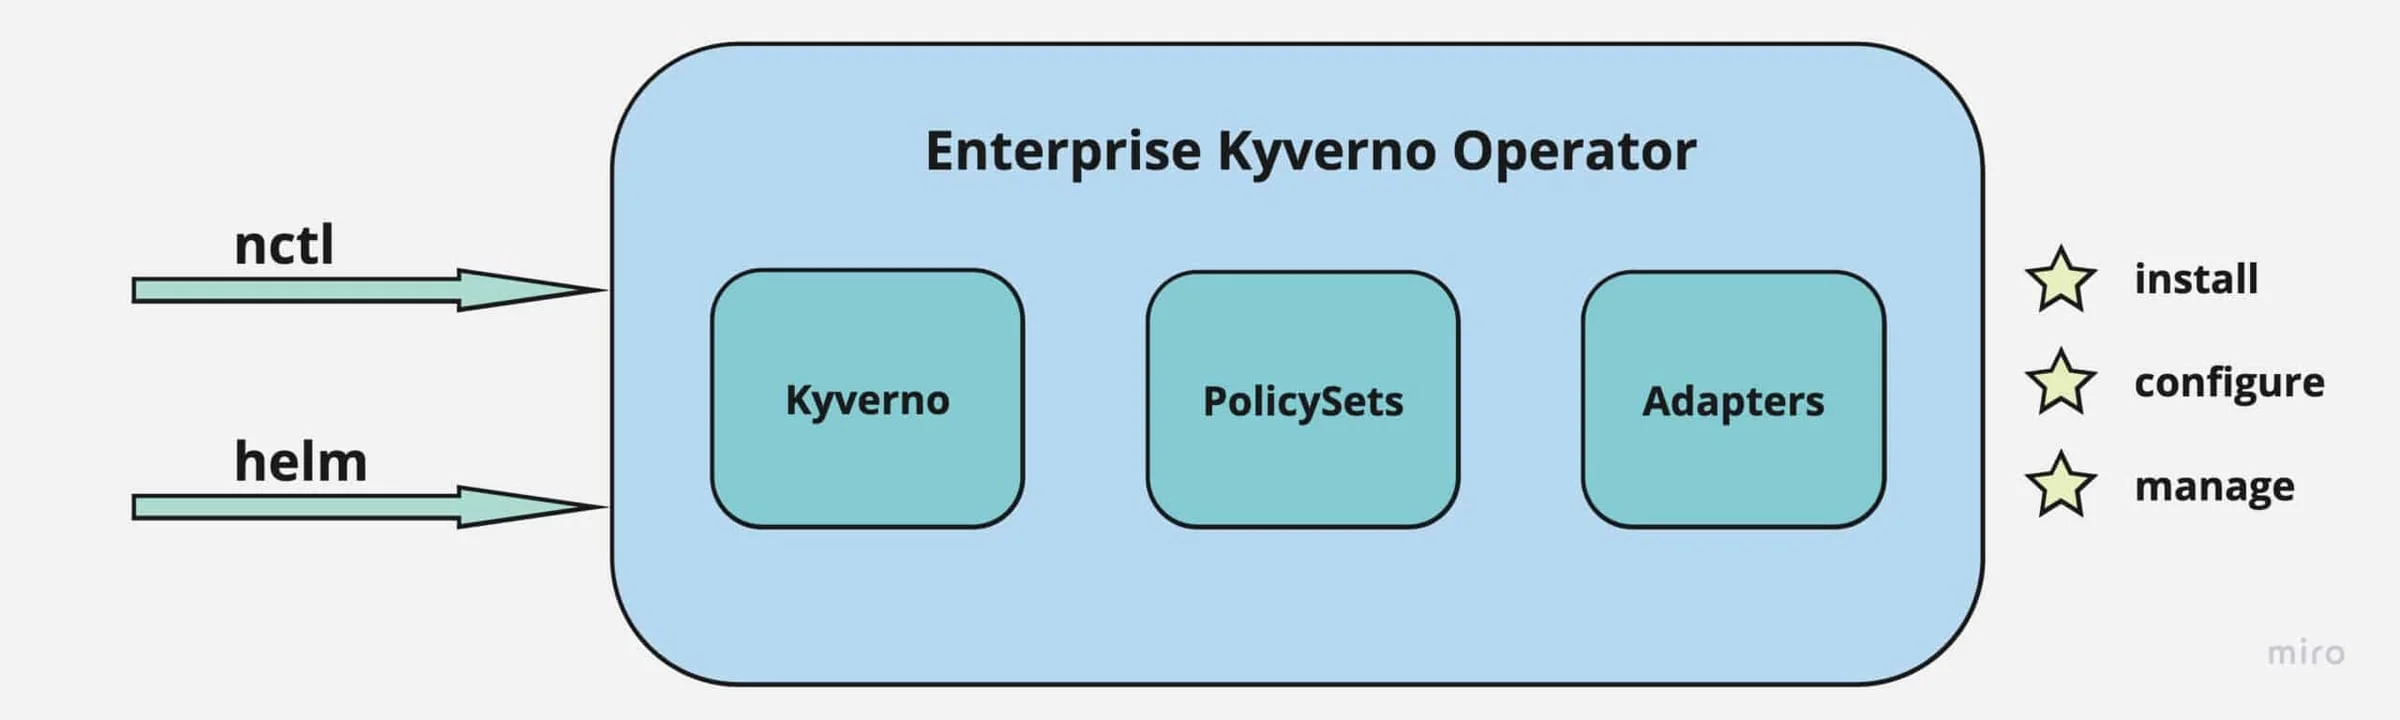
The Enterprise Kyverno Operator offers comprehensive lifecycle management capabilities that go beyond Kyverno itself, extending to related components like policies and…
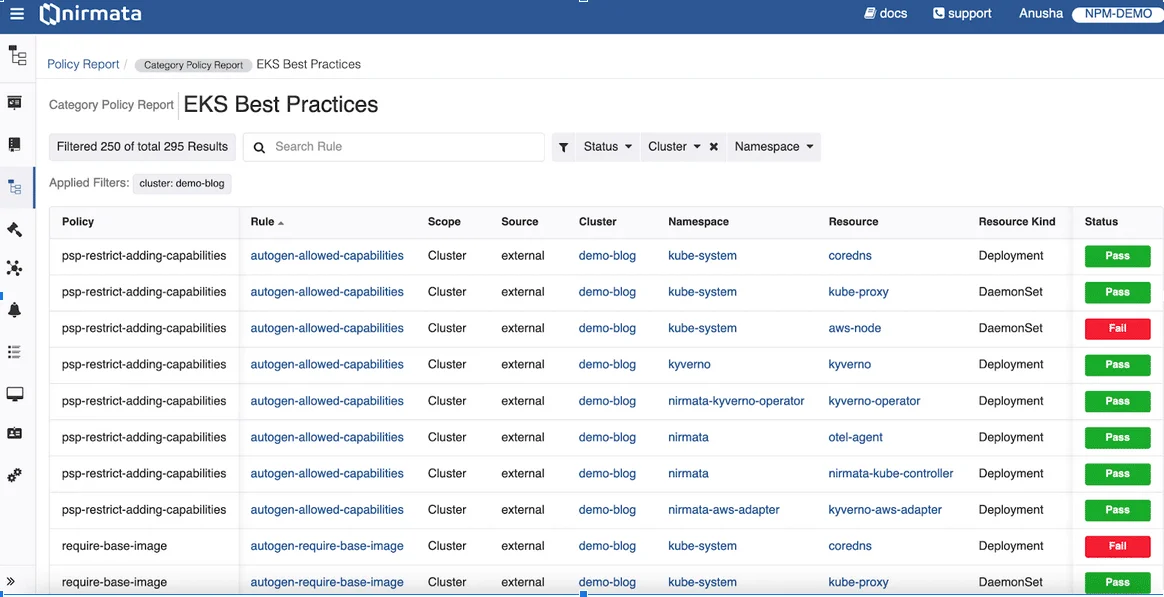
AWS provides suggestions to secure Amazon EKS clusters, but it’s crucial to enforce best practices and prevent misconfigurations to avoid unintended attacks. Kyverno by…